 In early 2013, WordPress installations around the world were subjected to global-scale brute force attacks.
These attacks were caused by botnets (computers infected with malware and programmed to attack other installations).
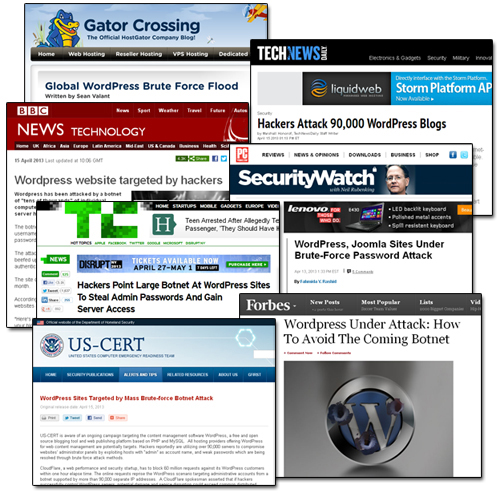
(WordPress powers millions of websites and blogs worldwide, making it a target for hacking attacks)
On March 11, 2014, many leading technology sites reported that over 162,000 WordPress web sites had been hacked.
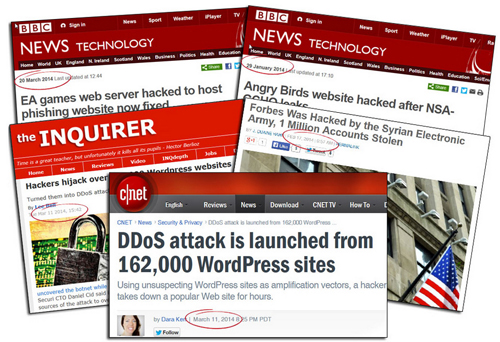
(160,000+ WordPress sites were attacked in a massive DDoS attack in March 2014. Screenshot: Blog Defender)
According to the Cnet report,
“With some old-fashioned trickery, hackers were able to get more than 162,000 legitimate WordPress-powered Web sites to mount a distributed-denial-of-service attack against another Web site.”
(Source: cnet.com/news/ddos-attack-is-launched-from-162000-wordpress-sites)
According to security firm Sucuri, hackers had leveraged a well-known flaw to attack unsuspecting WordPress web sites and direct a distributed-denial-of-service attack (DDoS) towards another popular website.
When worldwide attacks happen on WordPress sites, it’s natural for website owners to start questioning just how secure the WordPress platform is for building and running websites.
WordPress is often the target of malicious attacks by hackers. But do you really need to be concerned about WordPress as a secure web platform?
In this article, you will learn some of the main reasons why you should definitely consider using WordPress if you are at all concerned about website security.
WordPress Security Explained
Let’s start with some facts …
Thousands of websites and blogs are hacked every year … not just WordPress sites!
The sheer number of attacks on websites and blogs worldwide is increasing on a daily basis, and it’s only going to get worse.
It’s safe to assume that if your website or blog hasn’t been hacked yet, then it’s only a matter of time before someone does attempt to hack into your site … regardless of the web platform you use!
Since it’s not a matter of if, but when before your website is targeted by hackers, are there any advantages that WordPress can offer you in terms of security?
The “Open Source” Software Argument
Many people often argue that WordPress cannot be a safe platform for running a website or blog because having open source code means that anyone can view how the program works.
Open-source CMS software like WordPress, Drupal and Joomla are free to use and anyone has access to the underlying code.
The argument, then, goes something like this: If everyone can examine the Open Source software code for WordPress, then hackers can also easily download all of the code and go through all of it in detail, searching for security holes in the code that they can exploit …
(It’s no longer a matter of if, but when before someone tries to hack your website … WordPress or no WordPress!)
While it’s true that WordPress is a free program and hackers can easily access it and study the code looking for holes and weaknesses (hackers can do the same with any software program), the fact that WordPress is a free, open-source software platform actually makes it a whole lot more secure in many ways.
The reason for this is that WordPress is supported by a huge volunteer community comprised of hundreds of software programmers, plugin developers and theme designers who are constantly working to help to improve the platform and make WordPress more secure …
(With WordPress, a community of web developers worldwide is responsible for keeping the software code up-to-date. Source: WordPress.org)
WordPress evolves largely through the effort of hundreds of committed volunteers working around the clock to fix any issues detected by users. Everyone benefits from thousands of individuals dedicated to improving the code, identifying and fixing security issues and making the WordPress platform safer for every user …
(WordPress is built and maintained by a global community of web developers. Screenshot: make.wordpress.org)
The moment that a security vulnerability is identified by developers or users, these are normally logged in user forums and addressed by the WordPress development team …
(WordPress is continually being improved by thousands of committed individuals community of developers and users. Screenshot source: make.wordpress.org)
The WordPress community support system is solid and formidable and anybody can help contribute to the improvement of the software.
For example:
- If you discover bugs or security issues, you can report these by sending an email to security@wordpress.org.
- If you find issues in a WP plugin, you can report these by emailing plugins@wordpress.org.
This is why WordPress is constantly releasing new updates, and why you need to keep your WordPress sites and blogs updated and maintained …
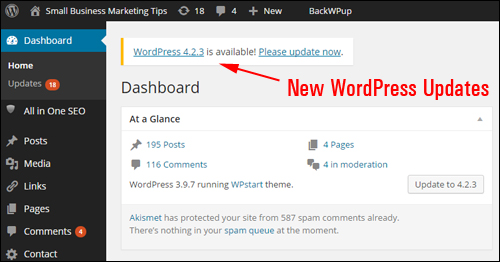
(WordPress frequently releases new updates to address any security issues found)
WordPress Vs Proprietary CMS Applications
Compare the benefits of using an open source CMS technology like WordPress with proprietary technologies where often the responsibility for maintaining software security, fixing bugs, etc. falls to a much smaller team of developers with limited resources and you will quickly realize the value and advantages of using WordPress to power your site on a secure platform.
The WordPress CMS is free to download, modify and use, and hundreds of volunteers and expert developers are continually working to improve the software. Can a proprietary technology company afford to employ as many developers and programmers and still deliver you software that is 100% free to download, use and modify as you wish?
WordPress CMS Vs Other Open Source Platforms
(CMS Platforms - WordPress, Joomla and Drupal)
Whilst on the topic of Open Source content management systems, research shows that WordPress is safer than other leading Open Source CMS platforms like Drupal and Joomla.
For example, here is one study showing the number of security vulnerabilities found in each of these open source platforms during a given period …
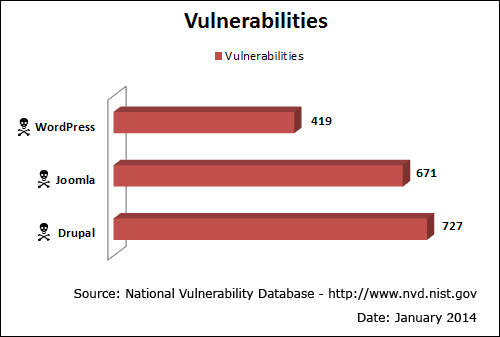
(National Vulnerability Database – Security Vulnerabilities IN CMS Applications. Image source: National Vulnerability Database)
Other research shows that, because WordPress is easy to use and keep updated, when sites across different CMS platforms were tested for security issues, sites run on WordPress had fewer exposure to risk …
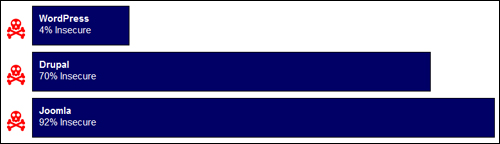
(Blog Defender – CMS Tests. Image: BlogDefender.com)
Don’t Blame The Technology
When WordPress sites get attacked, users shouldn’t be too quick to place the blame on the WordPress CMS platform.
According to a report called “Compromised Websites: An Owner’s Perspective,” published by security vendor Commtouch and StopBadware, a nonprofit organization that helps webmasters identify, remediate and prevent website compromises, a large number of webmasters are not fully aware of the security threats their websites are exposed to, how to properly secure a website, or deal with compromised web security.
In fact, 63% of webmasters surveyed in this report didn’t know how their websites were compromised by hackers after an attack …
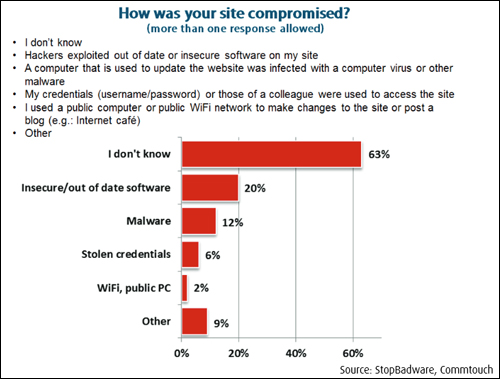
(Many webmasters don’t know how their sites were hacked. Screenshot image: StopBadware.org)
Of more immediate concern is the fact that most security-related problems result from site owners running WordPress on outdated versions of the software …
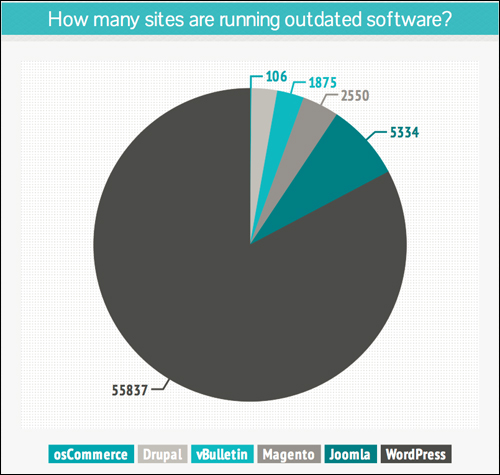
(Many security issues come from sites running an outdated version of WordPress. Screenshot source: Sucuri.net)
When WordPress security issues were examined in more detail, it was found that only a small percentage of vulnerabilities discovered in 3rd-party code are actually found in the WordPress CMS core, while 70% – 85% percent of all security issues are found in plug-ins and extensions …
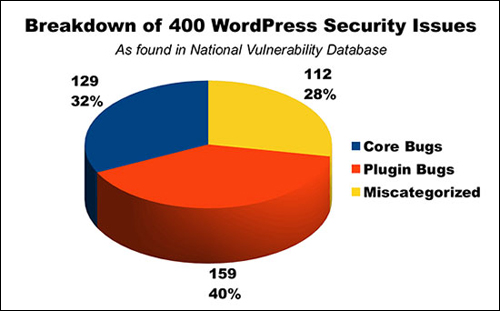
(WP Security Issues. Source: WebDesign.org)
Like all robust software platforms, WordPress is updated regularly to deal with new security risks that could arise. Improving software security is an ongoing concern, and to that end, you should always keep up to date with the latest version of WordPress software, plugins, themes, etc..
WordPress Is Secure – Even Banks Are Using It!
The amount of misinformation about how secure WordPress is has even caused Matt Mullenweg, the co-founder of WordPress, to chime into the online debate.
In an article entitled “A Bank Website on WordPress” published on April 15, 2015, Matt wrote the following about WordPress security …
There’s a thread on Quora asking “I am powering a bank’s website using WordPress. What security measures should I take?” The answers have mostly been ignorant junk along the lines of “Oh NOES WP is INSECURE! let me take my money out of that bank”, so I wrote one myself, which I’ve copied below.
I agree there’s probably not a ton of benefit to having the online banking / billpay / etc portion of a bank’s website on WordPress, however there is no reason you couldn’t run the front-end and marketing side of the site on WordPress, and in fact you’d be leveraging WordPress’ strength as a content management platform that is flexible, customizable, and easy to update and maintain.
Matt then goes on to provide a couple of security tips, before stating the following …
For an example of a beautiful, responsive banking website built on WordPress, check out Gateway Bank of Mesa AZ. WordPress is also trusted to run sites for some of the largest and most security-conscious organizations in the world, including Facebook, SAP, Glenn Greenwald’s The Intercept, eBay, McAfee, Sophos, GNOME, Mozilla, MIT, Reuters, CNN, Google Ventures, NASA, and literally hundreds more.
As the most widely used CMS in the world, many people use and deploy the open source version of WordPress in a sub-optimal and insecure way, but the same could be said of Linux, Apache, MySQL, Node, Rails, Java, or any widely-used software. It is possible and actually not that hard to run WordPress in a way that is secure enough for a bank, government site, media site, or anything.
Millions of businesses choose WordPress to build their presence online, including banks, global corporations, and e-commerce sites, not just bloggers.
Other Areas That Can Affect WP Blog Security
Other issues that can affect security include:
- No platform is immune to hackers. As many as 90% of all websites across all platforms are vulnerable to attack, mostly due to software that is out of date.
- The main security risk in all web platforms seems to be the users themselves. An example of this is users ignoring good password security recommendations.
- Lack of constant system monitoring. All security systems require constant monitoring, testing, updating and improvement.
- Webhosting server setup. For example, sites on shared hosting accounts are only as secure as the least secure site on the grid, so if another user on your shared server gets their site broken into, then every site on your server is potentially vulnerable to hacking also.
There Is No Reason Not To Choose WordPress
As this article has hopefully shown, WordPress is quite secure. As long as you commit to implementing basic website security measures (which all website owners should do, regardless of their chosen technology platform) and keep your WordPress software (and plugins, themes, etc.) regularly up-to-date, there’s really no reason why you shouldn’t choose WordPress for your web site or blog.

WordPress Security – Useful Tips
To learn about ways to protect your WordPress site from brute-force attacks see this article: Preventing WordPress From Brute Force Attacks
An unsecured website provides hackers with a valuable resource for launching distributed attacks, spreading malware and engaging in information theft. Blog Defender Security Plugin for WordPress Websites makes your WordPress site invisible to malicious attacks from hackers and bots. Learn more about this plugin here:
If you are currently using an older WordPress version make sure to make a backup before updating your software to protect your site from the latest security risks. This way, if something goes wrong, you can always restore.
If you don’t want to perform manual backups, there are many plugins you can use. You can read about a WordPress backup plugin that can fully automate your site backups here: Backup, Duplicate And Keep Your WordPress Web Site Protected With Backup Creator Plugin For WordPress

References Used In This Article
For more information on the above, refer to the sites below:
- ITProPortal.com
- National Vulnerability Database
- BlogDefender.com
- UpAndUpStudios.com
- StopBadware.org
- Sucuri.net
- WebDesign.org
- Quora.com
- Ma.tt
Hopefully, the above article has given you a better understanding of problems that can affect your website and how WordPress can help you grow your business online. To learn more about using WordPress please see other articles published on this site or subscribe to receive updates and notifications whenever new articles are published.
***
"I love the way your email series "Infinite Web Content Creation Training Series" is documented and presented. It is very absorbing and captivating. The links and tutorials are interesting and educational. This has motivated me to rewrite my content following the concepts I am learning from the email series." - Mani Raju, www.fortuneinewaste.com