 WordPress is frequently the target of malicious attacks by hackers.
In April 2013, WordPress installations around the world were subjected to a worldwide brute-force attack.
These attacks were caused by infected computer networks programmed to attack other vulnerable sites (botnets).
How To Protect Your WordPress Site From A Brute-Force Attack
What Is A Brute Force Attack?
A brute-force attack is a technique used to break an encryption or authentication system by trying all possibilities.
(Source: Chinese University Of Hong Kong)
One of the many ways hackers will attempt to break into a WordPress site is by trying to guess the site’s administration login username and password. This is achieved with software programs that can guess hundreds of possible logins in minutes.
If you’re using weak user names and passwords that are easy to guess, your site can be easily hacked by persistent attempts to guess your site’s login details.
This is called a “brute force” login attack.
What Is A Botnet?
A botnet is a number of Internet-connected computers communicating with other similar machines in an effort to complete repetitive tasks and objectives. This can be as mundane as keeping control of an Internet Relay Chat (IRC) channel, or it could be used to send spam email or participate in distributed denial-of-service attacks. The word botnet is a combination of the words robot and network.
(Source: Wikipedia)
A “Botnet” is a network of private computers that have been infected with malicious scripts or software code, which are then controlled remotely as a group, often without the unsuspecting computer owners even being aware that this is happening.
Botnets are normally used used to send mass spam emails from computers of unsuspecting users.
Below is a screenshot taken from an internet security monitoring site showing the locations of the command centers of a botnet that has been actively compromising computer networks all around the world since 2009 called “Zeus” …
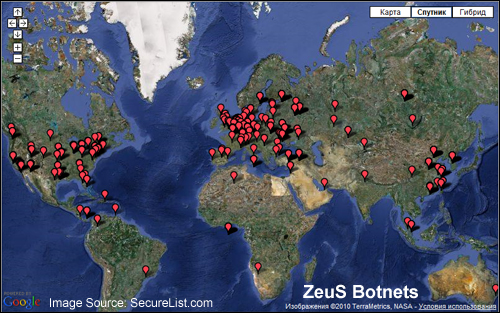
(The Zeus botnet has been actively compromising computer networks all around the world since 2009. Image: SecureList.com)
The ongoing botnet attacks on WordPress are highly distributed and well organized. Over 90,000 IP addresses were identified by a number of hosting companies in the initial attack, when the web was flooded with millions of attempts to force their way into WordPress user administration areas. The worldwide brute-force attacks then continued, with over 30,000 WordPress sites and blogs being hacked each day.
Coverage of this large-scale brute force attack was widely reported in all the major webhosting companies, as well as the leading technology publications, such as Forbes, TechNews Daily, Tech Crunch, BBC News, PC Magazine, and even on the official website of the US Department of Homeland Security …
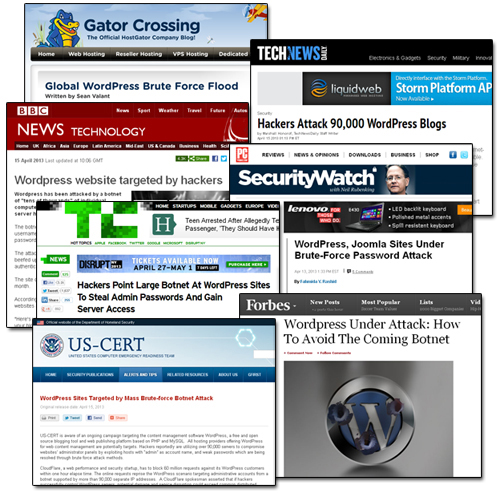
(Being the world’s most used CMS makes WordPress an obvious target for hacking)
Does This Mean We Shouldn’t Use WordPress Anymore?
No. In fact, there are many great reasons why you should choose WordPress if you are concerned about the security of your online presence.
To learn why WordPress is a secure web platform, read this article: Is WordPress A Secure Platform For Websites?

It’s important to note that, in the case of the brute-force botnet attack described above, there was actually no WordPress vulnerability being exploited (the same script was also targeting sites built using other web applications like Joomla).
Mike Little, the co-founder of WordPress, made this comment about the brute force attacks:
It is a “simple” script that attempts to login using the admin login and a generated password. So if your password is too short or based on dictionary words it will be guessed and then the script can login legitimately and do whatever it wants including installing scripts (as plugins) or editing files. The attack tries to guess your password, if it succeeds, the most secure site in the world is wide open because they have your password.
Protecting Your WordPress Blog From Being Brute Force Attacked – Ten Security Measures
You may think that your site is of little value to hackers, but the reality is that to a hacker, every website provides an opportunity to profit or benefit at your expense.
If a malicious user can discover a security weakness in your system that lets them take over your website, that web site can then be used as a “bot” in a planned cyber attack against larger and more highly-valued websites.
Additional undesirable effects of being hacked include getting blacklisted by Google, having stealthy spam links promoting things like casinos, porn, etc. inserted in your content and meta data, redirecting visitors to phishing sites, data exfiltration (stealing customer details or Personal Identifiable Information from your web applications), and lots of other nasty things.
The harsh reality is that hackers are probably trying to hack into your site right now. Whether they can be successful or not, depends on how difficult or easy you have made it for them to continue persisting until they work out a way to get in, or give up and decide to look for an easier target.
How Much Information About Your Site Are You Broadcasting To Hackers?
Do you own a WordPress site? If so, visit Hackertarget.com and run your site through their WordPress security check …
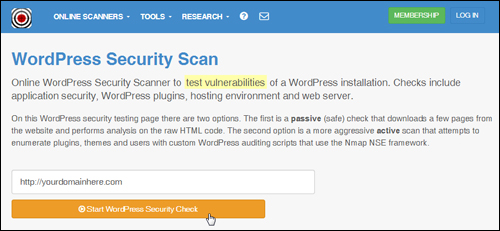 (Website Security Check Source: https://hackertarget.com/wordpress-security-scan)
You will see that the scan returns a number of results and details about your site …
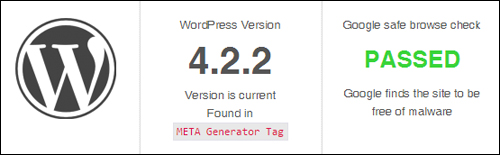
(website security check results. Screenshot: Hackertarget.com)
It should be obvious after using the above tool that if you are able to see all of this information about your site, hackers can too.
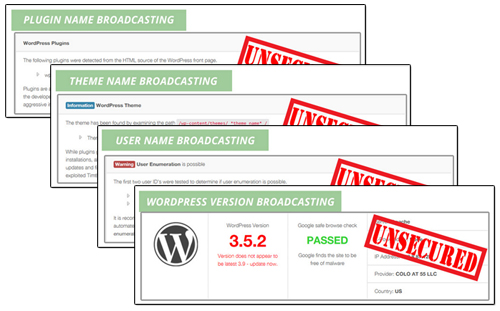 (Screenshot: Blog Defender)
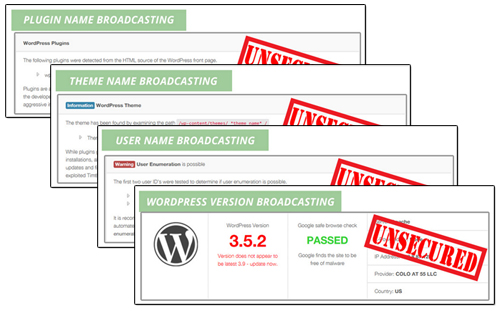
The ability to see which version of WordPress you are using, which plugins and themes you have installed on your site, and which files have been uploaded to certain directories in your site can be potentially valuable information to hackers, as this can inform them about potentially exploitable vulnerabilities, especially where site owners haven’t updated their software versions.
If your website is powered by WordPress and you’re not taking appropriate steps to bullet-proof your site, it’s practically guaranteed that, at some point in time, your site will be hacked, or at least targeted by bots, because these brute force attacks are systematically hitting WordPress sites worldwide!
When a site is hacked, webmasters will find themselves “locked out” of their own site, or notice that their content has been interfered with or even entirely wiped out. Typically, sites will become infected with malicious scripts without the owner even being aware that this has taken place.
To avoid the heartache that comes with having your website being hacked into, below are 10 essential and effective security measures that will help to prevent your WordPress site from being brute-force attacked.

Note: Some of the steps listed below need some technical understanding of how to modify core WordPress or server files. If you are not technical, or don’t want to mess around with code on your site, then ask your web host or search for a professional WordPress technical provider in our WordPress Services Directory.
***
Security Measure #1 – Contact Your Webhosting Service Provider
Get in touch with your host and ask them exactly what systems they offer to protect your site from being attacked, and what is done to ensure that your server files and data get regularly backed up.
It’s important to check that your hosting provider regularly backs up your server files and that, if anything should happen, you can quickly and easily get back your files.
Security Measure #2 – Back Up Your WordPress Data And Files And Keep Your Site Regularly Maintained
Never rely just on your hosting provider for site backups. Instead, learn how to maintain and manage your WordPress site or get this service done for you and develop a habit of religiously performing a full WordPress site maintenance routine frequently (e.g. daily, weekly, monthly, etc …)
A complete WordPress maintenance routine ensures that:
- All unnecessary files and data are removed,
- All files and data are free of errors, optimized and backed up,
- All WordPress plugins, themes and software components are up-to-date,
- etc …
A proper WordPress maintenance routine looks like this …
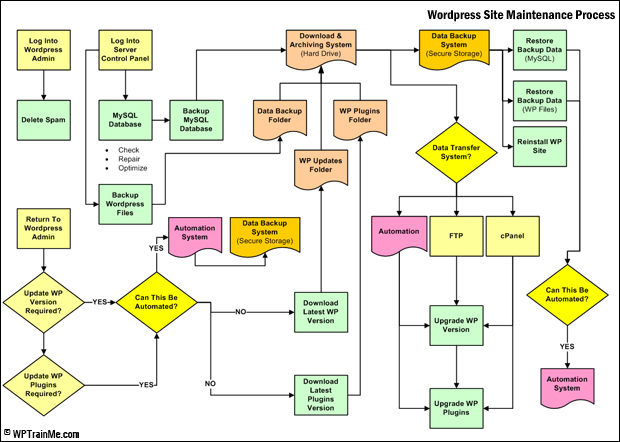 (Maintaining your WP web site regularly backed up and up-to-date is vitally important for WordPress security. Screenshot source: WPTrainMe.com)
Again, we cannot stress enough how vitally important maintaining your WordPress web site frequently backed up and updated is. WordPress site maintenance is not hard or time-consuming, but it must be done to ensure the security of your website. If you don’t want to learn how to do WordPress site maintenance yourself, pay someone to do it but make sure it gets done. Backing up your site is the next most important thing you should do after making sure that you are still breathing!
If you don’t want to back up your files manually, there are many plugins you can use. Learn about a WordPress backup plugin that can fully automate your backup process here: Backup, Clone And Keep Your WordPress Site Protected With Backup Creator WP Plugin
Security Measure #3 – Make Sure That Your Username Is Not “Admin”
The brute-force attack on WordPress sites was mostly attempting to compromise website administrator panels by exploiting installations using “admin” as their user name.
For reasons of website security, avoid setting up WordPress sites with the username admin. This is the first thing hackers will test. If your blog’s user name is “admin”, then make sure you change it immediately.
For a detailed step-by-step tutorial for WP admin users that shows you how to change your login username, go here: How To Change Your Admin Username In WordPress
Security Measure #4 – Make Sure Your Password Is Secure
A “brute force” attack occurs when malicious software persistently tries to guess the right password and username characters that will unlock your website.
Unless some measure is put into place to prevent the brute force attack (see further below for a couple of simple and effective ways to do this), the “bot” will just continue attacking your site until it eventually “cracks” the code.
Passwords that are easy to guess, therefore, are really easy targets for bot attacks. Make sure that you change your password combination to a string containing at least 8 or 9 characters long, and that includes upper and lowercase letters, combined with “special” characters (^%$#&@*).

Roboform is a password tool you can use to generate different hard-to-crack passwords …
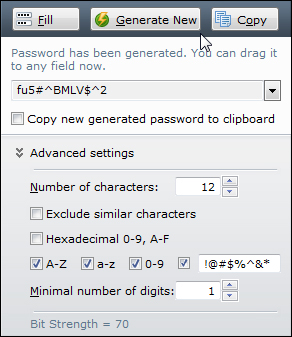 (You can use a password management tool like Roboform to help you generate strong login passwords)
For a tutorial for WordPress users on how to change your admin password, go here: What To Do If You Need To Change Passwords
Security Measure #5 – Prevent The wp-config.php File From Being Accessed
The wp-config.php file contains information about your WordPress site’s database and is used to define advanced options for WordPress.
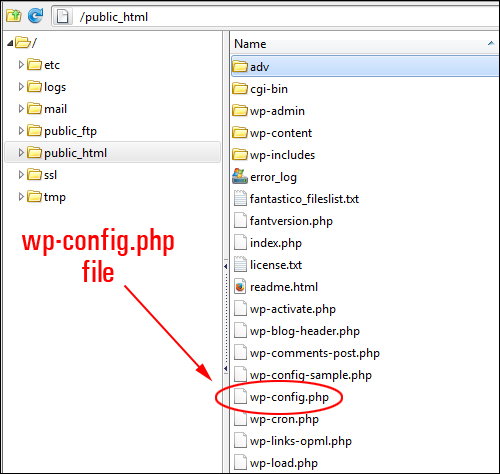
(WordPress WP Config file)
If hackers break into your site, they will normally try to access your wp-config.php file, because this is the file that contains important information about your site’s database, security keys, etc. Getting access to this information would allow them to change anything in your database, create a user account, upload files and take control of your site.
To protect your WordPress site from attacks and even being used as part of a bot net, therefore, you must prevent people accessing your wp-config.php file. This requires knowing how to edit database information, move files around in your server and changing access permissions.
Security Measure #6 – Rename Or Delete Unnecessary Installation Files
Delete or rename your install.php, upgrade.php and readme.html files.
You can remove these files after installation. If you don’t want to delete these files, just rename them.
Security Measure #7 – Keep Your WordPress CMS, Themes And Plugins Up-To-Date
Hackers look for vulnerabilities in older versions of WordPress that they can exploit, including out-of-date versions of WP plugins and themes.
Make sure to keep your WordPress application files, themes, plugins, etc. up-to-date.
Security Measure #8 – Disable The Theme Editor
WordPress comes with a built-in editor that allows site administrators to edit theme and plugin code from the dashboard area.
In WordPress, you can access your WordPress Theme Editor by selecting Appearance > Editor in your main menu …
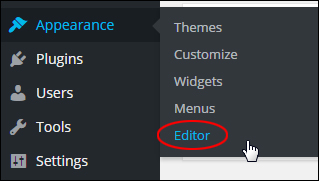
(Accessing the WordPress theme editor using the WordPress main menu)
The WordPress theme editor allows anyone accessing your site’s admin to view and edit your WP theme template files, and cause havoc on your site.
To prevent people from being able to access the WordPress Theme editor, you will need to disable it. This can be done by adding code to your wp-config.php file.
Security Measure #9 – Prevent Access To The Site’s Uploads Folder
The “uploads” folder stores all the media files that get uploaded to your blog.
Normally, this folder is visible to online users. All someone has to do to see the contents in your site’s “uploads” folder is navigate to your directory using a web browser …
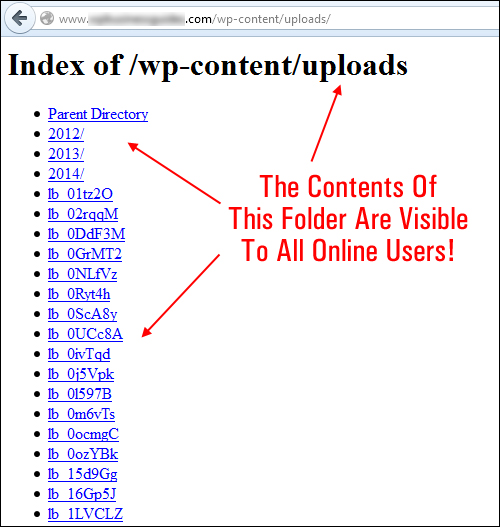
(WordPress uploads directory)
If any files stored in his folder have weaknesses or vulnerabilities that can be exploited by hackers, someone could upload unauthorized file types or compromise the security of your website.
Protecting your directories will prevent unauthorized people from accessing your ‘uploads’ folder and other important directories. This can be done using plugins, setting file permissions, uploading a blank index.php file (this is literally a blank file named “index.php”) to your uploads directory, and so on. Again, it’s best to get professional help if you are not sure about what to do.
Security Measure #10 – Security Plugins
Several security plugins for WordPress are available that will address most security issues faced by WordPress site owners, such as preventing unauthorized users from accessing your site, protecting your files from brute-force attacks, preventing unauthorized file uploads, etc.
Many WordPress plugins address some but not all areas of WordPress security. One WordPress security plugin that seems to do a comprehensive job of scanning, fixing and preventing issues that could lead to hackers accessing your files and causing irreparable damage to your site is SecureScanPro.
(SecureScanPro – WP complete security software)
SecureScanPro is easy to install and easy to use, and fixes most of the security areas that WordPress users need to address.
Another great plugin you may want to consider using is BlogDefender.
Blog Defender
 (Blog Defender Security Product Suite For WordPress Sites)
Blog Defender is a suite of WordPress security video tutorials, WordPress plugins and tools, plus a WordPress security PDF/DOC file.
BlogDefender shows you where potential security weaknesses in your WordPress installation are …
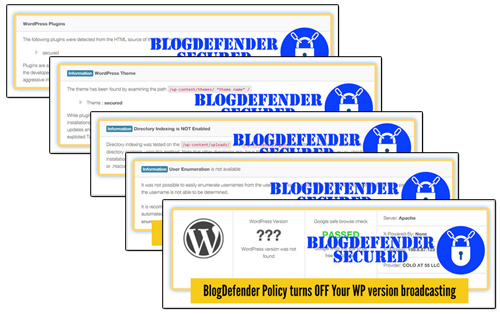
 And then shows you how to fix these quickly and easily …
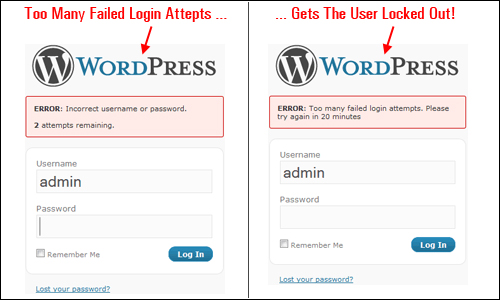
 If you don’t want to buy a security plugin like SecureScanPro or BlogDefender, you can use various free plugins, such as Limit Login Attempts …
WordPress is a secure platform, but neglecting simple maintenance tasks like updating your WordPress software, WordPress plugins and WP themes, tightening file and data protection and taking other necessary precautions can expose your website to attacks by hackers and bots.
No matter what kind of business you run or plan to run online and how small you think your web presence is, you simply cannot afford to ignore the importance of securing your web sites.
As a final reminder, below is the advice given by a web security expert to all WordPress users following the mass brute force attacks by botnets on WordPress in April 2013 …
Owners of websites based on WordPress CMS must improve at least basic security settings and implement best practices such as the use of robust passwords and the accurate management of “admin” accounts.
Pierluigi Paganini, Chief Information Security Officer, Security Affairs
***
As you can see, website security is of the utmost importance if you run a WordPress site. Hopefully, this article has shown you what to do to keep your WordPress site protected from brute force attacks. If you need any further help or assistance with WordPress security, please seek help from a professional WordPress security specialist, or search for a WordPress technical provider in our WordPress Services Directory.
We also recommend subscribing to WPCompendium.org to receive notifications via email whenever we publish new articles on WordPress security and reviews of new security plugins and solutions.
***
"I have used the tutorials to teach all of my clients and it has probably never been so easy for everyone to learn WordPress ... Now I don't need to buy all these very expensive video courses that often don't deliver what they promise." - Stefan Wendt, Internet Marketing Success Group
***