 In April 2013, WordPress installations around the world were subjected to a worldwide brute-force attack.
These attacks were caused by botnets (computers infected with viruses and programmed to attack other vulnerable installations).
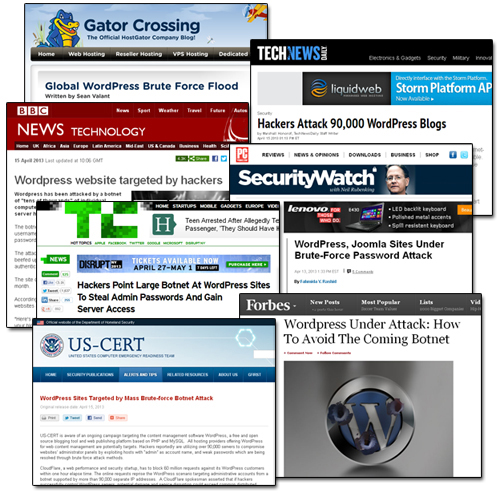
(WordPress is the world’s most used content management system making it a target for malicious attempts by hackers)
In March 2014, many leading technology sites reported that over 160,000+ WordPress-powered web sites had been hacked.
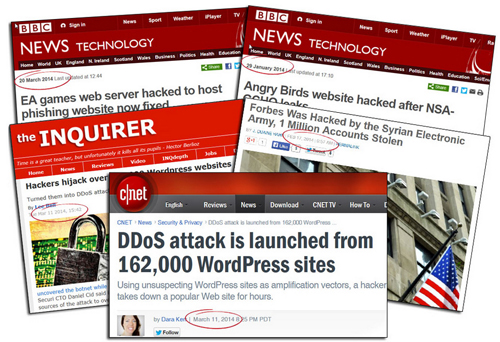
(Over 160,000 WordPress sites were attacked in a massive DDoS attack in early 2014. Screenshot: Blog Defender)
According to the Cnet report,
“With some old-fashioned trickery, hackers were able to get more than 162,000 legitimate WordPress-powered Web sites to mount a distributed-denial-of-service attack against another Web site.”
(Source: cnet.com/news/ddos-attack-is-launched-from-162000-wordpress-sites)
As reported by security firm Sucuri, hackers had leveraged a flaw to attack unsuspecting WP sites and direct a distributed-denial-of-service cyberattack (DDoS) towards another popular website.
Whenever global brute force attacks happen on WordPress sites, it’s natural for people to question just how safe and secure the WordPress platform is for building and running their websites.
WordPress is the world’s most used CMS which makes it a target for attempted hacker attacks. But should you be concerned about WordPress as being a secure web platform?
In this article, you will learn some of the main reasons why you should consider using WordPress if you are at all concerned about website security.
WordPress Security Explained
Let’s start by looking at some facts …
Thousands of websites and blogs are hacked every year … not just WordPress sites!
The scale of attacks on websites and blogs worldwide is rising, and things are getting worse.
It’s safe to assume that if you haven’t been hacked yet, then it’s only a matter of time … regardless of the web platform your website has been built with!
Since it’s not a matter of if, but when before someone attempts to hack your website, are there any advantages that WordPress can offer you in terms of security?
How Secure Are “Open Source” Applications?
Many people will often argue that WordPress is not a safe platform for running a business online because it is “open source” and freely available program.
Open-source CMS software like WordPress, Drupal and Joomla are free to use and anyone can have access to the entire underlying software code.
The argument against using WordPress, then, goes something like this: If everyone can examine the Open Source software code for WordPress, then hackers can also easily get hold of the code and go through it in great detail, searching for security weaknesses in the code that can be exploited …
(It’s no longer a matter of if, but a matter of when before a malicious user attempts to hack your website … WordPress or no WordPress!)
While it’s true that WordPress is a free program and hackers can easily access it and study the code looking for weaknesses and vulnerabilities that can be exploited (hackers can do the same with any software), the fact that WordPress is a free, open application actually makes it a lot more secure in a number of ways.
The reason for this is that WordPress has the support of a volunteer community that consists of hundreds of people such as software programmers, plugin developers and theme designers who constantly help to improve the software and make WordPress more secure …
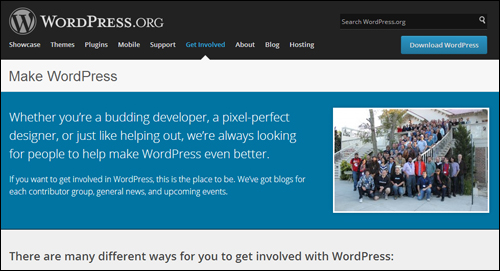
(With WordPress, a community of developers around the world is responsible for keeping the platform maintained and updated. Source: WordPress.org)
WordPress continually evolves because of the effort of hundreds of committed volunteers working around the clock to fix any issues detected by users. It benefits from thousands of individuals who, at any one time, are focused on improving the code, identifying and fixing security vulnerabilities and making WordPress safer for every user …
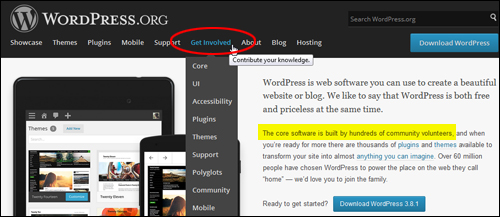
(The WordPress core software is built and maintained by a global community of users. Screenshot image: WordPress.org)
The moment any security issues are identified by developers or users, these are reported in user forums and addressed by the WordPress development team …
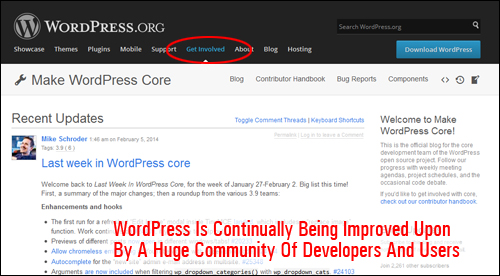
(WordPress is continually being improved by thousands of committed individuals community of developers and users. Source: make.wordpress.org)
The WordPress community support system is solid and formidable and anybody can help contribute to the process of addressing vulnerabilities.
For example:
- If you find bugs and security holes, you can report these by notifying security@wordpress.org.
- If you find any issues in a plugin, you can also report these by sending an email to plugins@wordpress.org.
This is the reason why the WordPress community is constantly releasing new security updates, and why you continually need to keep your WordPress sites and blogs frequently updated …
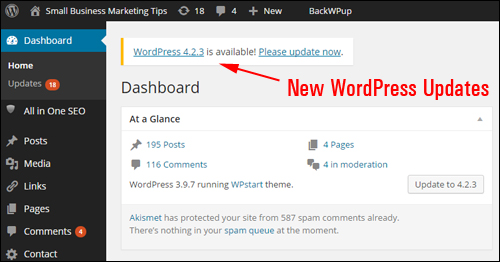
(WordPress frequently releases new updates to address any security weaknesses found)
WordPress CMS Vs Proprietary Applications
We’ve just seen that one of the security advantages of using an open source platform like WordPress is that users benefit from a large community of developers who continually contribute to improve code security. By contrast, a proprietary or “closed-source” software application would normally be built by a small team of developers with limited time and resources to provide continuous security monitoring, support, bug fixes and updates.
WordPress is 100% free to download, use and modify, and thousands of volunteers and expert developers are continually working to improve the platform. Can a proprietary technology company afford to employ as many developers and programmers and still deliver you a free application that you can download, use and modify as you wish?
WordPress CMS Vs Other Open Source CMS Platforms
(CMS Platforms)
Whilst on the topic of Open Source content management applications, research shows that WordPress is safer than other leading Open Source CMS platforms such as Drupal and Joomla.
For example, the chart below shows the number of security vulnerabilities found in each of these open source platforms during a certain period …
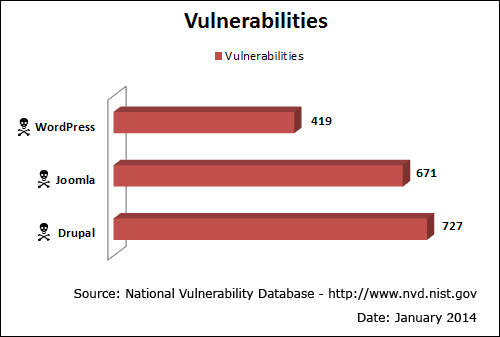
(National Vulnerability Database – Security Vulnerabilities IN CMS Applications. Screenshot source: National Vulnerability Database)
Other studies also show that, because WordPress is quite easy to use and keep updated, when sites using different CMS platforms were tested for security issues, sites run on WordPress had fewer exposure to risk …
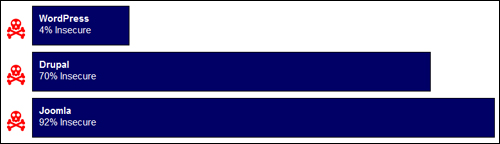
(Blog Defender – CMS Tests. Screenshot image: BlogDefender.com)
Don’t Blame WordPress When Things Go Wrong
If someone hacks into your WordPress site, don’t be too quick to blame WordPress.
According to security organizations Commtouch and StopBadware in a published report entitled “Compromised Websites: An Owner’s Perspective“, most website owners have no idea about the security threats their websites are exposed to, how to secure a website, or how to deal with web security compromises.
In fact, 63% of webmasters surveyed in this report didn’t even know how their websites were hacked after an attack …
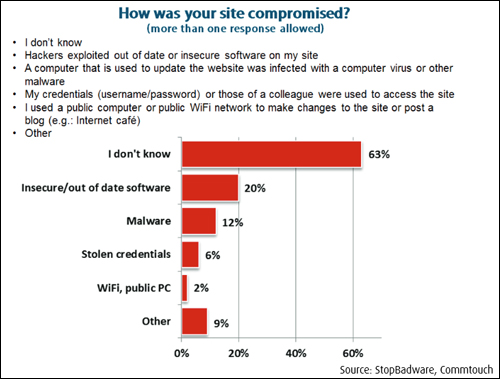
(Many webmasters don’t even know how their sites were hacked. Source: StopBadware.org)
Of more immediate concern is the fact that most security problems seem to be related to website owners simply not updating their WordPress software to the latest version …
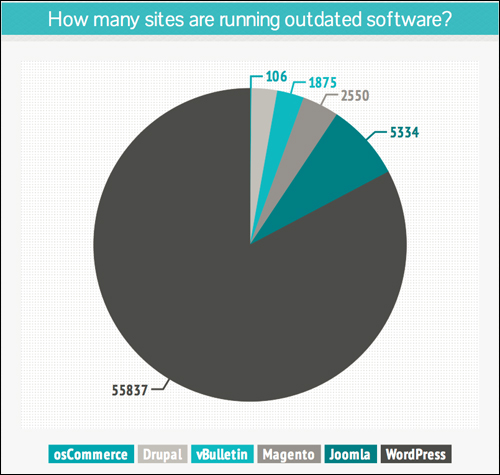
(Many WordPress users have not upgraded their software. Image source: Sucuri.net)
When WordPress security issues were examined in more detail, it was found that only a small percentage of vulnerabilities discovered in third-party code are found in the WordPress core software, while most security issues are found in plug-ins and developed externally for WordPress …
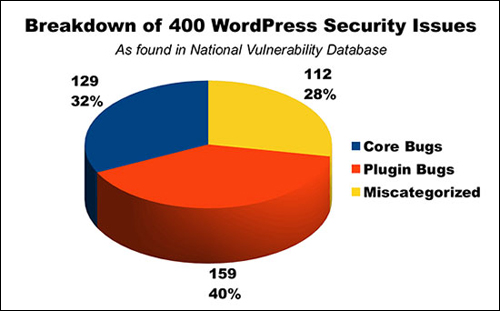
(WordPress Security Issues. Screenshot: WebDesign.org)
Like many software applications, WordPress is regularly updated to deal with new security risks that could arise. Improving software security is always a concern, and to that end, you should always keep your WordPress software, themes, and plugins updated to the latest version.
WordPress … Secure Enough For Banks To Use!
The amount of misinformation online about WordPress security has even led the co-founder of WordPress, Matt Mullenweg, to chime into the debate.
In a blog post entitled “A Bank Website on WordPress” posted on April 15, 2015, Matt wrote the following about WordPress security …
There’s a thread on Quora asking “I am powering a bank’s website using WordPress. What security measures should I take?” The answers have mostly been ignorant junk along the lines of “Oh NOES WP is INSECURE! let me take my money out of that bank”, so I wrote one myself, which I’ve copied below.
I agree there’s probably not a ton of benefit to having the online banking / billpay / etc portion of a bank’s website on WordPress, however there is no reason you couldn’t run the front-end and marketing side of the site on WordPress, and in fact you’d be leveraging WordPress’ strength as a content management platform that is flexible, customizable, and easy to update and maintain.
Matt then goes on to provide a couple of security tips, before stating the following …
For an example of a beautiful, responsive banking website built on WordPress, check out Gateway Bank of Mesa AZ. WordPress is also trusted to run sites for some of the largest and most security-conscious organizations in the world, including Facebook, SAP, Glenn Greenwald’s The Intercept, eBay, McAfee, Sophos, GNOME, Mozilla, MIT, Reuters, CNN, Google Ventures, NASA, and literally hundreds more.
As the most widely used CMS in the world, many people use and deploy the open source version of WordPress in a sub-optimal and insecure way, but the same could be said of Linux, Apache, MySQL, Node, Rails, Java, or any widely-used software. It is possible and actually not that hard to run WordPress in a way that is secure enough for a bank, government site, media site, or anything.
Millions of businesses around the world, including banks, large organizations and e-commerce sites choose WordPress to build their presence online, not just bloggers.
Other Areas That Can Affect Security
Other areas that can affect WordPress security include:
- No platform is immune to hacking. As many as 90% of all websites across all platforms are vulnerable to being attacked, mostly due to using outdated software.
- The main risk of all web platforms seems to be the users themselves. For example, many users ignore good password security recommendations.
- Lack of constant system monitoring. Security processes need to be constantly monitored, tested, updated and improved.
- Hosting setup. For example, websites on shared webhosting are only as safe as the least secure website on the grid, so if someone else has a weak FTP password on your shared server, then every site on the shared server is potentially vulnerable.
There’s No Reason Why You Shouldn’t Choose WordPress
As you can see, WordPress is as secure as most other leading web platforms being used by businesses to build their presence online. As long as you continue to implement basic security measures and keep your WordPress software (and plugins, themes, etc.) regularly up-to-date, there’s no reason to avoid using WordPress for your website or blog.

WordPress Security – Useful Tips
To learn about ways to protect your WordPress site from brute force attacks see this article: How To Prevent Brute Force Attacks On Your WordPress Site Or Blog
A vulnerable blog offers malicious users with a valuable resource for denial of service attacks, spreading malware and engaging in information theft. Blog Defender Security Plugin for WordPress Sites makes your WordPress site invisible to botnets and hackers. Learn more about it here:
If you are currently using an older WordPress version remember to back up your site files and data before updating your software to protect your site from the latest security risks. This way, if something goes wrong, you can always restore your web site or blog to its former configuration.
If you don’t want to perform manual backups, there are a number of WordPress plugins you can use. You can read about a WordPress backup plugin that can automate your site backups here: Back Up, Duplicate And Protect Your WP Website With Backup Creator WordPress Plugin

Article References
For more information on the above, refer to the sites below:
- ITProPortal.com
- National Vulnerability Database
- BlogDefender.com
- UpAndUpStudios.com
- StopBadware.org
- Sucuri.net
- WebDesign.org
- Quora.com
- Ma.tt
Hopefully, this post has given you a better understanding of issues that can affect your website and how WordPress can help you improve your business online. To learn more about using WordPress please see our related posts section or subscribe to receive updates and notifications when new articles are published.
***
"Wow! I never knew there's so much to learn about WordPress! I bought one of the WordPress for Dummies three years ago, such authors need to be on this course!" - Rich Law, Create A Blog Now