 In early 2013, WordPress installations around the world were subjected to a global-scale brute-force attack.
These attacks were caused by computers infected with malware and programmed to attack other sites (called “botnets”).
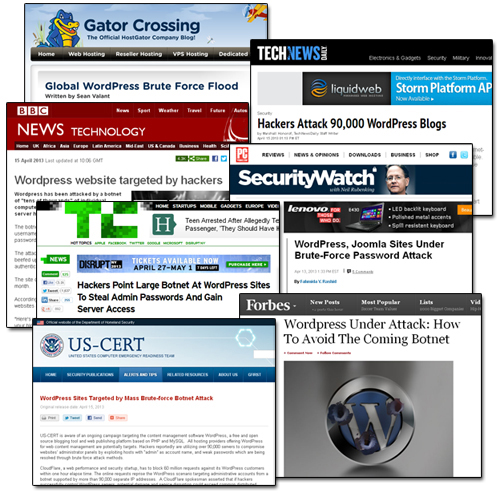
(Being the world’s most used content management system makes WordPress an obvious target for hacking attempts)
On March 11, 2014, technology sites reported that over 162,000 WordPress sites had been hacked.
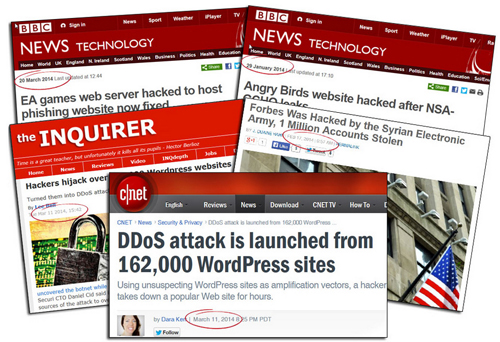
(Over 160,000 WordPress sites were attacked in a massive DDoS attack in early 2014. Screenshot image: Blog Defender)
According to the Cnet report,
“With some old-fashioned trickery, hackers were able to get more than 162,000 legitimate WordPress-powered Web sites to mount a distributed-denial-of-service attack against another Web site.”
(Source: cnet.com/news/ddos-attack-is-launched-from-162000-wordpress-sites)
As reported by security firm Sucuri, hackers had leveraged a flaw to attack unsuspecting WordPress web sites and direct a distributed-denial-of-service cyber attack (DDoS) towards another popular website.
Whenever worldwide attacks happen on WordPress sites, it’s natural for people to ask if WordPress really is a secure software for building and running their sites.
WordPress powers millions of websites around the world, making it a target for hacking attacks. But should you really be concerned about WordPress as being a secure web platform?
In this article, you will learn some of the main reasons why you should definitely consider choosing WordPress if you are at all concerned about website security.
WordPress Security Explained
Let’s start by looking at some facts …
Thousands of websites and blogs are attacked every year … not just WordPress sites!
The scale of attacks on websites and blogs around the world is massive, and this is only going to get worse.
You can safely assume that if you haven’t been hacked yet, then it’s only a matter of time … regardless of the web platform your website has been built with!
Since it’s not a matter of if, but a matter of when before a malicious user will try to hack your website, are there any advantages that WordPress can offer you in terms of security?
How Secure Is “Open Source” Software?
Some people will often try and argue that WordPress should not be used for running a website or blog because its open source code means that anyone can view how the software program runs.
Open source CMS software like WordPress, Drupal and Joomla are free to use and anyone can view the underlying software code.
The argument against using WordPress, then, goes something like this: If anyone can access the Open Source code for WordPress, then hackers can also easily download all of the code and study every single line in great detail, looking for weaknesses and vulnerabilities that they can exploit …
(It’s no longer a matter of if, but a matter of when before someone will attempt to hack your website … WordPress or no WordPress!)
While it’s true that WordPress is a free program and hackers can easily go through the code searching for security vulnerabilities and weaknesses (hackers can do the same with any program), the fact that WordPress is a free, open-source software platform actually makes it a whole lot more secure in several ways.
The reason for this is that WordPress is supported by a global community of thousands of people such as software programmers, plugin developers and theme designers who are constantly working to help to improve the platform and make WordPress more secure …
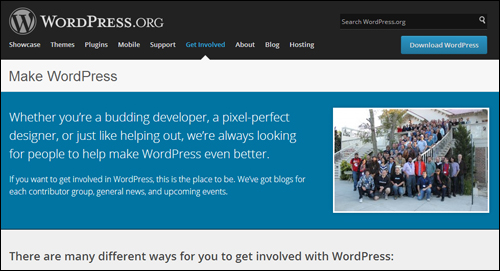
(With WordPress, a global community of web developers is responsible for keeping the platform updated. Screenshot source: make.wordpress.org)
WordPress evolves through the effort of hundreds of committed volunteers working around the clock to fix issues. It benefits from thousands of minds who, at any one time, are focused on improving the software, fixing bugs and making the WordPress platform safer for every user …
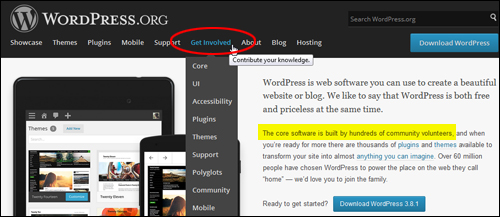
(The WordPress core software is built by a global community of contributors. Image source: make.wordpress.org)
As soon as a security weakness is identified by developers or users, these are recorded in user forums and addressed by the WordPress core developers …
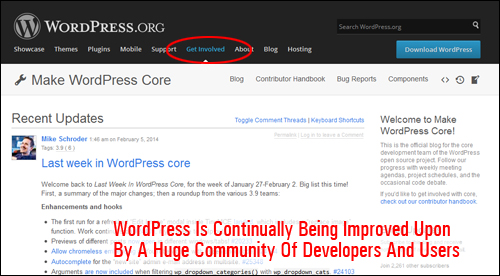
(WordPress is continually being improved upon by a global community community of users and web developers. Image: WordPress.org)
The WordPress community support system is solid and formidable and anybody can help contribute to fixing the software.
For example:
- If you find bugs or security holes, you can report these by notifying security@wordpress.org.
- If you find issues in a WP plugin, you can also report these by sending an email to plugins@wordpress.org.
This is one of the reasons why WordPress is constantly releasing new updates, and why you continually need to keep your sites and blogs up-to-date …
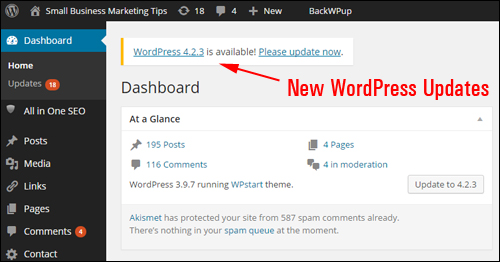
(WordPress continually releases new updates to address any security issues found)
WordPress Vs Proprietary CMS Platforms
We’ve just seen that one of the security advantages of using an ”open” platform like WordPress is that users benefit from a large community of developers who continually contribute to make the code more secure. By contrast, a proprietary or “closed-source” CMS application is built by a small team of developers with limited time and resources to provide continuous security monitoring, maintenance services, bug fixes and updates.
WordPress is free to download, modify and use, and hundreds of volunteers and expert developers work on improving the platform. Can a proprietary technology company afford to employ as many developers and programmers and still deliver you software that is 100% free to download, use and modify as you wish?
WordPress Vs Other Open Source CMS Platforms
(CMS Platforms - WordPress, Joomla and Drupal)
Whilst on the topic of Open Source content management systems, research shows that the WordPress CMS is actually safer than other Open Source CMS platforms like Drupal and Joomla.
For example, here is one study showing how many security vulnerabilities were discovered in each of these platforms during a certain period …
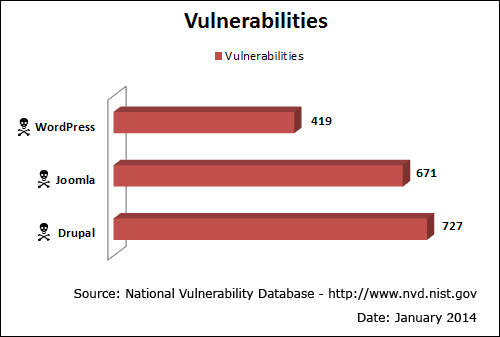
(WordPress experiences fewer security vulnerabilities than other leading CMS applications. Image source: National Vulnerability Database)
Other research shows that, because WordPress is easy to use and keep updated, when sites across different CMS platforms were tested for security vulnerabilities, sites built with WordPress had less exposure to risk …
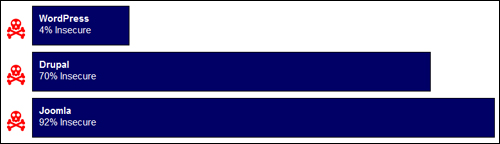
(WordPress users are less exposed to security threats than other CMS platform users. Image source: BlogDefender.com)
Don’t Blame WordPress When Things Go Wrong
If someone hacks into your WordPress site, don’t be quick to blame WordPress.
According to a report called “Compromised Websites: An Owner’s Perspective,” which is published by security vendor Commtouch and StopBadware, a nonprofit organization that helps webmasters identify, remediate and prevent website compromises, a large number of website owners have no idea about the security threats their websites are exposed to, how to properly secure a website, or deal with web security compromises.
In fact, over sixty percent of webmasters surveyed in this report didn’t know how their websites were hacked after an attack …
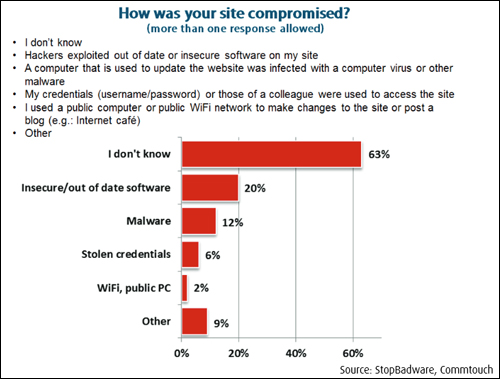
(Most webmasters don’t even know how their sites were hacked. Source: StopBadware.org)
Of more immediate concern, however, is the fact that most security-related issues arise from site owners running WordPress on outdated versions of the software …
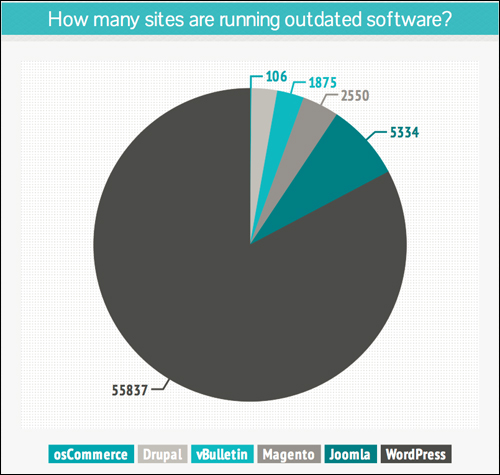
(Many WordPress users have not upgraded their WP sites. Screenshot source: Sucuri.net)
When WordPress security issues were looked at in more detail, it was found that only a small percentage of vulnerabilities discovered in third-party code are found in the WordPress CMS core, while most security issues are found in plug-ins and developed externally …
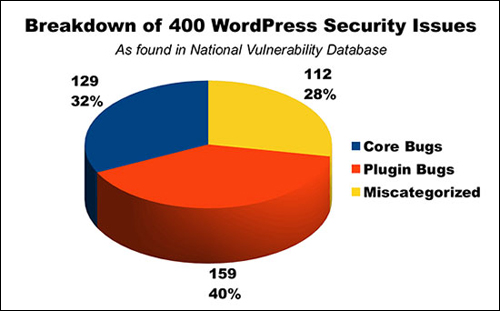
(WP Security Issues. Source: WebDesign.org)
Like many web applications, WordPress is updated regularly to address new security vulnerabilities that could arise. Improving software security is an ongoing concern, and to that end, you should always keep your WordPress site, plugins, and themes up-to-date.
WordPress Is Secure – Just Ask Any Bank Using It!
The amount of misinformation online about how secure WordPress is has even caused Matt Mullenweg, the co-founder of WordPress, to chime in and reply to posts online.
In a post entitled “A Bank Website on WordPress” posted on April 15, 2015, Matt wrote the following about WordPress …
There’s a thread on Quora asking “I am powering a bank’s website using WordPress. What security measures should I take?” The answers have mostly been ignorant junk along the lines of “Oh NOES WP is INSECURE! let me take my money out of that bank”, so I wrote one myself, which I’ve copied below.
I agree there’s probably not a ton of benefit to having the online banking / billpay / etc portion of a bank’s website on WordPress, however there is no reason you couldn’t run the front-end and marketing side of the site on WordPress, and in fact you’d be leveraging WordPress’ strength as a content management platform that is flexible, customizable, and easy to update and maintain.
Matt then goes on to provide a couple of security tips, before stating the following …
For an example of a beautiful, responsive banking website built on WordPress, check out Gateway Bank of Mesa AZ. WordPress is also trusted to run sites for some of the largest and most security-conscious organizations in the world, including Facebook, SAP, Glenn Greenwald’s The Intercept, eBay, McAfee, Sophos, GNOME, Mozilla, MIT, Reuters, CNN, Google Ventures, NASA, and literally hundreds more.
As the most widely used CMS in the world, many people use and deploy the open source version of WordPress in a sub-optimal and insecure way, but the same could be said of Linux, Apache, MySQL, Node, Rails, Java, or any widely-used software. It is possible and actually not that hard to run WordPress in a way that is secure enough for a bank, government site, media site, or anything.
Millions of businesses around the world, including banks, large organizations and e-commerce sites choose WordPress to build their web presence, not just bloggers.
Other Areas Affecting Security
Other areas that can affect security include:
- No platform is safe from hacking. As many as 90% of all websites across all platforms are vulnerable to being attacked, mostly due to using software that is out of date.
- The biggest security risk in all content management systems seems to be the users themselves. An example of this is users ignoring strong password security practices.
- Lack of constant system monitoring. Security systems need frequent monitoring, testing, updating and improvement.
- Server setup. For example, websites on shared hosting are only as safe as the least secure website on the hosting grid, so if someone else on your shared server gets their site hacked into, then all sites on that server can potentially become vulnerable to being hacked also.
There’s No Reason Not To Choose WordPress
As this article has hopefully shown, WordPress is as secure as most of the leading web platforms being used by businesses of all sizes to build their presence online. As long as you remember to implement basic web security measures (which all website owners should do) and keep your WordPress software (and themes, plugins, etc.) updated, there’s no reason to avoid using WordPress to run your web site or blog.

WordPress Security – Useful Tips
To learn about ways to protect your WordPress site from brute-force attacks see this article: Preventing WordPress Brute Force Attacks
A compromised web site provides malicious users with a resource for distributed attacks, spreading malware and as a source of information theft. Blog Defender WordPress Security Plugin makes your WordPress site invisible to botnet and hacker attacks. Go here to learn more:
If you are currently using an outdated WordPress version remember to back up everything before updating your software to benefit from the latest security updates. This way, if things don’t go as planned, you can always restore your web site or blog to its former settings.
If you don’t want to back up your files manually, there are many free and paid plugins you can use. Learn about a WordPress backup plugin that can fully automate your site backups here: Backup, Duplicate And Keep Your WordPress Websites And Blogs Protected With Backup Creator WP Plugin

References Used In This Article
For more information on the above, see the following sources:
- ITProPortal.com
- National Vulnerability Database
- BlogDefender.com
- UpAndUpStudios.com
- StopBadware.org
- Sucuri.net
- WebDesign.org
- Quora.com
- Ma.tt
Hopefully, now you have a better understanding of issues that can affect your website and how WordPress can help you build a better business online. To learn more about the security benefits of using WordPress for a business website please click on links to visit our related posts section or subscribe to receive updates and notifications when new articles or tutorials are published.
***
"I love the way your email series "Infinite Web Content Creation Training Series" is documented and presented. It is very absorbing and captivating. The links and tutorials are interesting and educational. This has motivated me to rewrite my content following the concepts I am learning from the email series." - Mani Raju, www.fortuneinewaste.com