 Being the world’s most used CMS makes WordPress a frequent target for attempted attacks by hackers.
In 2013, WordPress installations around the world were subjected to worldwide brute force attacks.
These attacks were caused by botnets (computer networks infected with viruses and programmed to attack other vulnerable computers).
How To Protect Your WordPress Site From A Brute-Force Attack
Brute Force Attacks
A brute-force attack is a technique used to break an encryption or authentication system by trying all possibilities.
(Source: Chinese University Of Hong Kong)
One of the many ways hackers will attempt to break into a WordPress site is by trying to guess the site admin’s login username and password. To achieve this, hackers use software programs and scripts that automatically tries to guess hundreds of possible logins in minutes.
If you’re using obvious user names and passwords that are easy to guess, your website can be easily hacked by repeated attempts to work out your site’s login details.
This is called a “brute-force” attack.
Botnets – What Are They?
A botnet is a number of Internet-connected computers communicating with other similar machines in an effort to complete repetitive tasks and objectives. This can be as mundane as keeping control of an Internet Relay Chat (IRC) channel, or it could be used to send spam email or participate in distributed denial-of-service attacks. The word botnet is a combination of the words robot and network.
(Source: Wikipedia.org)
A “Botnet” is a network of computers that have been compromised and infected with malicious code or scripts, which are then controlled remotely as a group, often without the unsuspecting computer owners’ knowledge or awareness.
Botnets are normally used used to send out mass spam emails.
Below is a screenshot taken from a site that monitors online security showing the locations of the command centers of a botnet that has been actively compromising computer networks all around the globe since 2009 called “Zeus” …
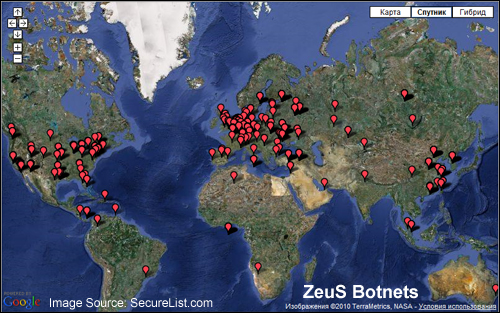
(ZeuS is a botnet that has been actively compromising computer networks all around the world since 2009. Image source: SecureList.com)
These botnet attacks are highly distributed and well organized. Over 90,000 IP addresses were identified by a number of webhosting companies in the initial attack alone, when millions of attempts to force their way into WordPress user administration areas took place. The large-scale attack continued after this, with over 30,000 WordPress blogs being hacked each day.
Coverage of the large-scale brute force botnet attack was reported by all of the major webhosting companiesand leading technology media publications, such as TechNews Daily, Forbes, BBC News, PC Magazine, Tech Crunch, and even on the official website of the US Department of Homeland Security …
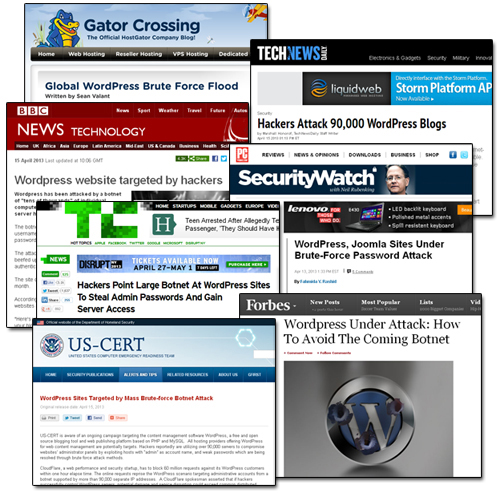
(WordPress is often the target of worldwide attacks by hackers)
Does This Mean WordPress Is Not Secure And We Should Stop Using It?
No. In fact, there are many good reasons why you should choose WordPress if you are concerned about the security of your web presence.
To understand why WordPress is a secure platform for websites, read this article: Is WordPress A Secure Platform For Websites?

It’s important to understand that, in the case of the worldwide brute force botnet attack described above, was no specific vulnerability in WordPress being exploited (the same script was also attacking sites built using applications like Joomla).
Mike Little, the co-founder of WordPress with Matt Mullenweg, said this about the brute-force attacks:
It is a “simple” script that attempts to login using the admin login and a generated password. So if your password is too short or based on dictionary words it will be guessed and then the script can login legitimately and do whatever it wants including installing scripts (as plugins) or editing files. The attack tries to guess your password, if it succeeds, the most secure site in the world is wide open because they have your password.
Preventing Your WordPress Site From Brute Force Attacks – 10 Security Measures
Every website or blog with a vulnerability offers some value to hackers. All websites have some value to hackers. Corporate sites, personal blogs, government web sites … even websites owned by web security and anti-hacking experts can and have been targeted.
If hackers can hack and gain control of your site, your web site can then be used as part of a larger network of “bots” to target other highly-valued sites.
Additional undesirable results of having your site hacked and your site security compromised include being blacklisted by Google, having stealthy spam links promoting things like casinos, porn, etc. inserted into your content and page title and descriptions, redirecting visitors to phishing sites or other websites, data exfiltration (stealing information or Personal Identifiable Information from your web applications), and lots of other nasties.
The truth is that hackers are probably looking for exploits and trying to break into your web site at this very moment. Whether they can get in successfully depends on how hard you will make it for them to continue persisting until they can either work out how to break in, or are forced to give up and decide to look for an easier target.
How Much Information About Your Site Are You Broadcasting To Hackers?
If you visit Hackertarget.com and run your site through their WordPress security scan …
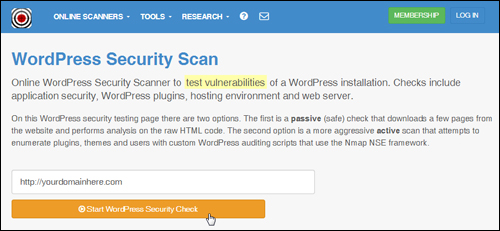 (Hackertarget – WordPress Security Scan Product image source: Hackertarget.com)
You will see that the test returns a number of results and details about your website …
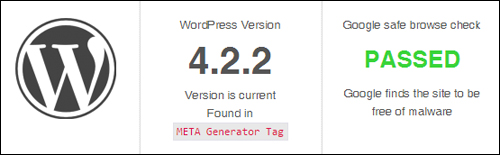
(Hackertarget – WP security scan results. Product image: Hackertarget.com)
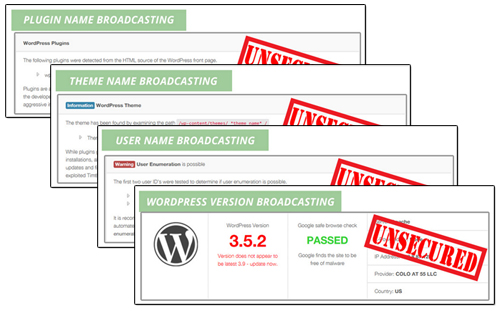
It should be obvious after using the above tool that if you are able to see all of this information about your WordPress site, so can hackers.
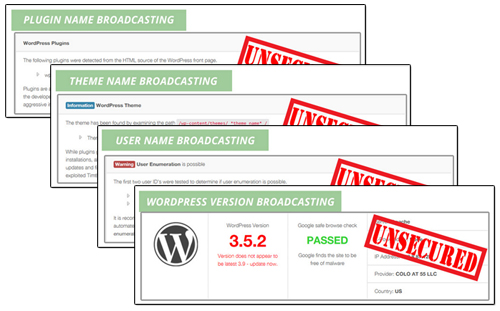 (Source: BlogDefender site)
Being able to see which version of WordPress you are using, which plugins and themes you have installed, and which files have been uploaded to certain directories on your server can be valuable information to hackers, as this informs them about any exploitable security weaknesses, especially in older versions.
If your site or blog is powered by WordPress and you’re not taking appropriate steps to harden your site, then it’s practically guaranteed that, at some point in time, someone will attempt to hack your installation, because these attacks are systematically targeting WordPress installations worldwide!
Whenever a site gets broken into, webmasters will discover much to their dismay that they have been “locked out” of their own site, or notice that their files have been altered or even that their content has been entirely wiped out. Typically, most compromised sites will be infected with malicious scripts without the owner’s knowledge or awareness.
To help avoid the heartache and aggravation (and potential loss of valuable business data) of discovering that your website has been hacked into, below are 10 essential and effective security measures that will help to protect your WordPress site from brute-force attacks.

Note: A few of the recommended measures shown below require some technical understanding of how to modify core WordPress and/or server files. If you have no web coding skills, or don’t want to mess around with file code, then ask your web host or a professional WordPress technical provider for assistance.
***
Security Measure #1 – Contact Your Web Host
Contact your hosting company and ask them what systems have been put into place to protect your site from being attacked, and what is done to ensure that your server files get regularly backed up.
Check that your hosting service regularly backs up your server files and that, if anything happens, you can quickly and easily recover your files.
Security Measure #2 – Perform Complete WordPress Backups And Keep Your Website Or Blog Frequently Maintained
You should never rely on your webhosting provider for site backups. Instead, learn how to manage your WordPress site or get this done for you and maintain a habit of religiously performing a full WordPress site maintenance routine on a frequent basis (e.g. weekly, fortnightly, etc …)
A full WordPress maintenance routine ensures that:
- All unnecessary data and files are removed,
- All WP data and files are free of errors, optimized and backed up,
- All WP software, themes and plugins are up-to-date,
- etc …
A proper WP site maintenance routine looks like this …
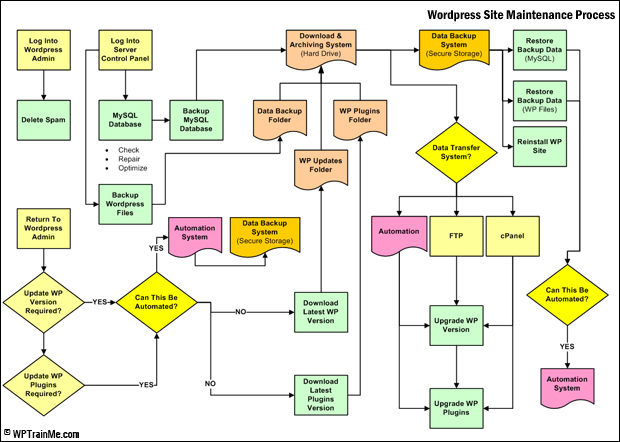 (Maintaining your WordPress site frequently backed up and up-to-date is vitally important for WordPress security. Image: WPTrainMe.com)
Again, we cannot stress enough how vitally important maintaining your WP website or blog regularly backed up and updated is. WP site maintenance is not hard or time-consuming, but it must be done to ensure the security of your website. If you don’t want to learn how to do WordPress maintenance yourself, pay someone to do it but make sure this gets done. Backing up your website is the next most important thing you must do after making sure that you still have a pulse!
If you don’t want to perform manual backups, there are a number of plugins you can use. You can read about a WordPress backup plugin that can automate your site backups here: Backup, Copy And Keep Your WP Websites And Blogs Protected With Backup Creator Plugin For WordPress
Security Measure #3 – Do Not Use “Admin” As A Username
The large scale brute force botnet attack on WordPress sites was mostly an attempt to compromise website administrator panels by exploiting sites that used “admin” as their account name.
For website security reasons, avoid setting up a WordPress site with the username “admin”. This is the first area hackers will test. If your blog’s user name is “admin”, you will should change this immediately.
We have created a simple tutorial on how to change your login username here: Changing Your WordPress User Name From Admin To A Different User Name
Security Measure #4 – Choose A Strong Password
A “brute force” attack occurs when a malicious script persistently tries to guess the right password and username character string that will unlock your site.
Unless you put some measure in place to prevent the brute-force attack (see further below for a couple of effective ways to do this), the “bot” will just keep attacking your site until it eventually “cracks” the code.
Passwords that are easy to guess, therefore, become very easy targets for hacking attacks. Make sure that you change your password to something containing at least 8 or 9 characters long, with both upper and lowercase letters, combined with “special” characters (%^#$@&*).

You can use a password program like Roboform to create passwords …
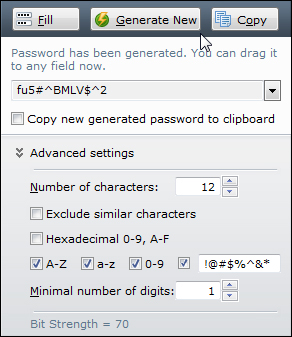 (You can use a password software tool like Roboform to help you generate strong passwords)
We have created a detailed tutorial that shows you how to change your login password here: What To Do If You Need To Change Passwords
Security Measure #5 – Prevent The wp-config.php File From Being Accessible
The wp-config.php file allows WordPress to communicate with the database to store and retrieve data and is used to define advanced options for WordPress.
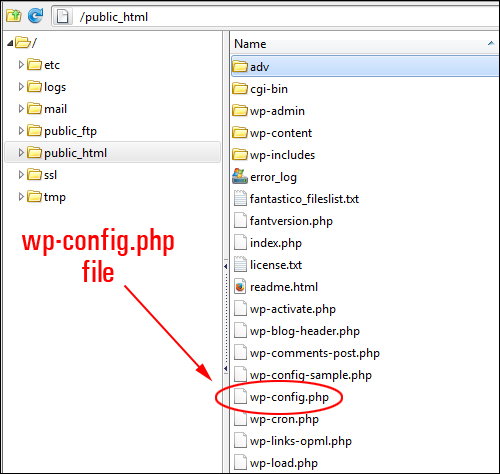
(WP Config file)
If a hacker breaks into your WordPress website, they will typically try to access the wp-config.php file, because this is the file that contains important information about your site’s database, security keys, etc. Getting access to this information would allow them to change anything in your database, create a user account, upload files and take control of your site.
To protect your WordPress site from attacks and even being used as part of a bot net, therefore, prevent your wp-config.php file from being easily accessible. This requires knowing how to edit database information, move files around in your server and changing access permissions.
Security Measure #6 – Delete Or Rename Unnecessary Website Installation Files
Rename or delete your install.php, upgrade.php and readme.html files.
You can remove these files after installation. If you don’t want to delete these files, just rename them.
Security Measure #7 – Keep Your WordPress Files, Themes And Plugins Up-To-Date
Hackers are always on the lookout for vulnerabilities in earlier versions of WordPress that can be exploited, including out-of-date versions of WP plugins and themes.
Make sure to always keep all of your application files, themes, plugins, etc. up-to-date.
Security Measure #8 – Disable Your Theme Editor
WordPress comes with a built-in editor that lets you edit plugin and theme code inside the dashboard.
You can access the WordPress Theme Editor by selecting Appearance > Editor in the dashboard menu …
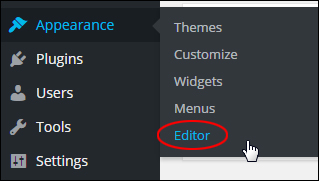
(The WordPress theme editor is accessible via the WordPress main menu)
This means that anyone logging into your site can view and change your WordPress theme files, or cause havoc on your site.
If you want to prevent people from accessing your WordPress Theme editor, you will need to disable it. This can be done by editing your wp-config.php file.
Security Measure #9 – Secure Your WordPress Uploads Folder
The WordPress “uploads” directory contains all the media files that get uploaded to your blog.
By default, this folder is visible to all users online. All someone has to do to see the contents stored in the “uploads” directory is navigate to your directory using their web browser …
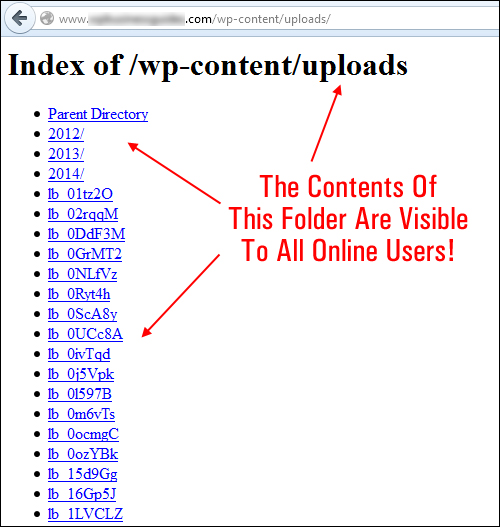
(WordPress uploads folder)
If any files stored in his folder have weaknesses or vulnerabilities that can be exploited by malicious users, anyone can upload unauthorized file types or compromise the security of your site.
Protecting your directories will prevent online users from accessing your ‘uploads’ folder and other important directories. This can be done using plugins, setting file permissions, adding a blank index.php file (this is literally an empty file called “index.php”) to your uploads directory, and so on. Again, it’s best to get professional help if you are unsure about what to do.
Security Measure #10 – WordPress Security Plugins
A number of great security plugins for WordPress are available that will address many common security issues faced by WordPress website owners, such as preventing hackers from gaining access to vital information about your site, protecting your website from malicious software, preventing unauthorized file uploads, etc.
Most WordPress plugins address some but not all areas of WordPress security. One security plugin that does a comprehensive job of scanning, fixing and preventing issues that could lead to hackers accessing your files and causing irreparable damage to your site is SecureScanPro.
(SecureScanPro – WP security plugin)
SecureScanPro is easy to install and easy to use, and does a great job of fixing most of the security areas that WordPress users need to address.
Another great plugin you may want to consider using is BlogDefender.
Blog Defender Security Plugin For WordPress Websites & Blogs
 (Blog Defender)
This product is a suite of WordPress security video tutorials, plugins and tools, plus a WordPress security PDF/DOC file.
BlogDefender scans you web site for potential security holes …
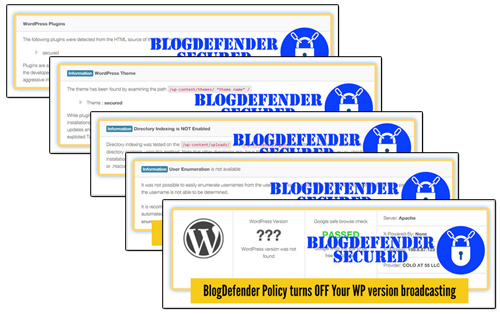
 And then shows you how to quickly fix these …
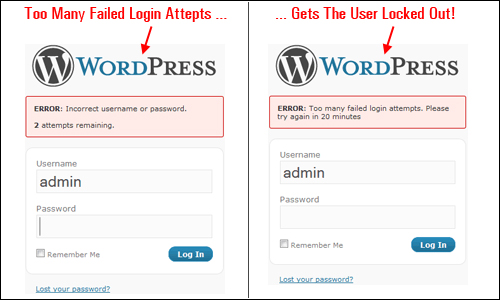
 If you don’t want to buy a premium security plugin like SecureScanPro or BlogDefender, then use various free plugins, such as Limit Login Attempts …
WordPress is a secure platform, but neglecting basic maintenance tasks like keeping your WordPress software, plugins and WP themes updated to their latest versions, tightening file and data protection and taking other necessary precautions can expose your website to attacks by hackers and bots.
No matter what type of business you run or plan to run online and how small you think your web presence is, website security is something you simply cannot afford to ignore.
As a final reminder, below is the advice given by a web security expert to all WordPress users following the large-scale brute-force attacks by botnets on WordPress in 2013 …
Owners of websites based on WordPress CMS must improve at least basic security settings and implement best practices such as the use of robust passwords and the accurate management of “admin” accounts.
Pierluigi Paganini, Chief Information Security Officer, Security Affairs
***
As you can see, website security is of the utmost importance if you run a WordPress site. Hopefully, the information in this article has shown you what to do to keep your WordPress site protected from brute-force attacks. If you need any further help or assistance with WordPress security, please seek help from a professional WordPress security specialist, or search for a professional WordPress service provider in our WordPress Services Directory.
Also, do yourself a favor and subscribe to WPCompendium.org to be notified whenever we publish new tips on WordPress security and tutorials about WordPress security plugins and solutions.
***
"Your training is the best in the world! It is simple, yet detailed, direct, understandable, memorable, and complete." Andrea Adams, FinancialJourney.org
***