 When you are the world’s most popular CMS platform and the preferred online publishing platform for millions of businesses and loved by thousands of web developers and website designers, it’s inevitable that at some point in time, WordPress will come under attack by hackers.
In early 2013, WordPress installations around the world were subjected to large-scale brute force attacks.
These attacks were caused by botnets (computer networks infected with malware and programmed to attack other computers with security vulnerabilities).
How To Protect Your WordPress Site From A Brute-Force Attack
About Brute Force Attacks
A brute-force attack is a technique used to break an encryption or authentication system by trying all possibilities.
(Source: Chinese University Of Hong Kong)
One of the many ways hackers use to try and break into a WordPress site is by trying to guess the site’s administration login username and password. To attempt this, hackers use scripts and tools that can guess hundreds of possible login combinations in minutes.
If you’re using weak user names and predictable passwords, your site could be easily hacked by a malicious script’s repeated attempts to work out your site’s login details.
This is called a “brute-force” login attack.
Botnets
A botnet is a number of Internet-connected computers communicating with other similar machines in an effort to complete repetitive tasks and objectives. This can be as mundane as keeping control of an Internet Relay Chat (IRC) channel, or it could be used to send spam email or participate in distributed denial-of-service attacks. The word botnet is a combination of the words robot and network.
(Source: Wikipedia.org)
A “Botnet” is a network of private computers that have been compromised and infected with malicious code, which can then be controlled remotely as a group, often without the computer owners even being aware that this is going on.
Botnets are typically used to blast out mass spam emails.
Below is a screenshot taken from an online security monitoring site showing the locations of the command centers of a botnet that has been actively compromising computer networks all around the world since 2009 called “Zeus” …
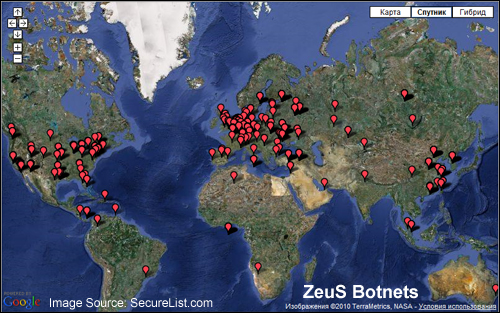
(ZeuS is a botnet that has been actively compromising computer networks all around the world since 2009. Source: SecureList.com)
The botnet attacks on WordPress sites were well organized and highly distributed. Over 90,000 IP addresses were identified by several webhosting companies in the initial attack, when the web was flooded with millions of attempts to force their way into WordPress users administration areas. The attacks then continued, with over 30,000 WordPress sites and blogs being hacked every day.
Coverage of the April 2013 brute-force botnet attack was reported by all of the major webhosting companiesand leading technology publications, such as Forbes, TechNews Daily, PC Magazine, Tech Crunch, BBC News, and even on the official website of the US Department of Homeland Security …
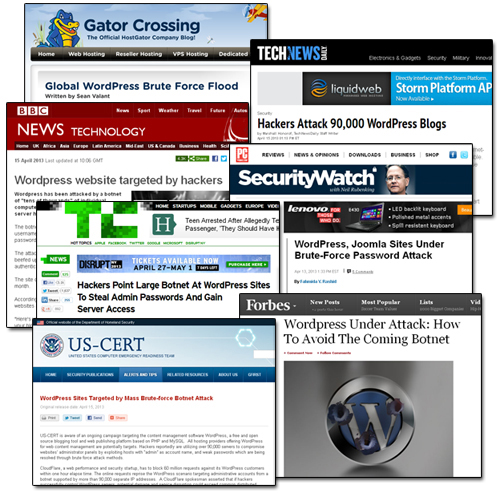
(Being the world’s most used CMS makes WordPress an obvious target for hacking)
Does This Mean We Should Stop Using WordPress?
No. In fact, there are lots of very good reasons why you should choose WordPress if you are concerned about the security of your online business.
To understand why WordPress is a secure web platform, see this article: Can You Build A Secure Business Online Using WordPress?

It’s important to understand that, in the case of the brute force attack described above, no specific WordPress vulnerability was being exploited (the same script was also attacking sites built using applications like Joomla).
Mike Little, one of the co-founders of WordPress with Matt Mullenweg, made this comment about the botnet attacks:
It is a “simple” script that attempts to login using the admin login and a generated password. So if your password is too short or based on dictionary words it will be guessed and then the script can login legitimately and do whatever it wants including installing scripts (as plugins) or editing files. The attack tries to guess your password, if it succeeds, the most secure site in the world is wide open because they have your password.
Preventing Your WordPress Website From Being Brute Force Attacked – Ten Security Points
Every site with a vulnerability has potential value to hackers. A vulnerable site provides malicious users with a platform for DDoS attacks, spreading malware and engaging in information theft.
If hackers can break in and compromise the control of your website, the website or blog can then be employed as a “bot” to attack more valued websites.
Additional undesirable impacts of having your website hacked and your site security compromised include being blacklisted by search engines, having spammy links advertising things like viagra, porn, etc. in your content and meta data, malicious redirects to phishing sites and other websites, drive-by downloads (adding malicious programs on your visitors’ computers), and lots of other nasties.
The truth is that hackers are very likely looking for security exploits and trying to break into your web site right now. Whether they can break into your site or not, depends on how hard or easy you can make it for hackers to keep persisting until they can either work out how to break in, or are forced to decide to look for an easier target.
How Much Information About Your Site Are You Broadcasting To Hackers?
Does your website run on WordPress? If so visit Hackertarget.com and run your site through their WordPress security check …
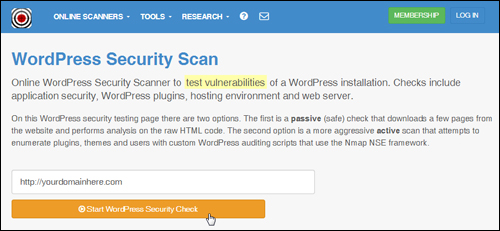 (WP Security Scan Screenshot source: https://hackertarget.com/wordpress-security-scan)
You will see that the test returns various results and details about your site …
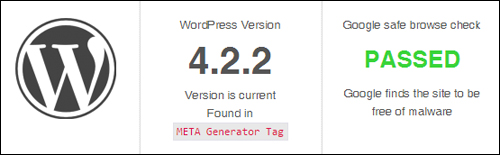
(website security scan results. Product image: Hackertarget.com)
It should be obvious after using the tool shown above that if you are able to see all of this information, then hackers can too.
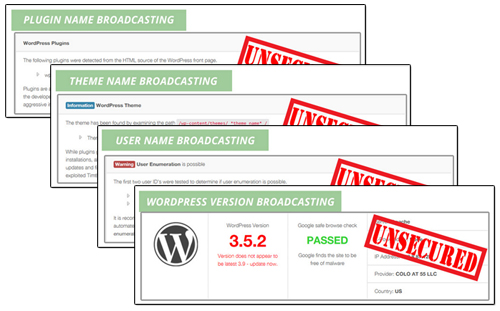 (Product image: BlogDefender.com)
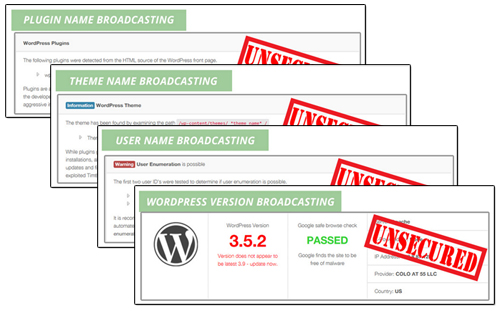
The ability to see which version of WordPress you are using, which plugins and themes you have installed on your site, and which files have been uploaded to certain directories are all potentially valuable information to hackers, as these can inform them about any exploitable security vulnerabilities, especially in older versions.
If your website is driven by WordPress and you’re not precautionary steps to harden your site, we can practically guarantee that, at some point, your site will be hacked, or at least targeted by bots, because these brute force attacks are systematically targeting WordPress sites around the world!
Typically, when a site is hacked, webmasters can find themselves “locked out” of their own site, or notice that their files have been modified or even that their content has been entirely wiped out. Often, most sites will become infected with malicious software without the owner even being aware that a breach has taken place.
To avoid the heartache and aggravation (and significant loss of valuable business data) that comes with discovering that your web site has been hacked into, below are 10 simple, yet essential and effective security checks that will help to protect your WordPress site from being attacked by brute force botnets.

Note: Some of the recommended measures below need some technical understanding of how to modify core WordPress and/or server files. If you have no web skills, or don’t want to mess around with code on your site, then ask your web host or search for a professional WordPress technical provider in our WordPress Services Directory.
***
Security Measure #1 – Get In Touch With Your Webhosting Service
Get in touch with your web host and ask them what systems are in place to protect your site from botnet attacks, and what they do to ensure that your WordPress sites get regularly backed up.
Make sure that your hosting company is regularly backing up your server files and that, if disaster strikes, you can easily get back your site.
Security Measure #2 – Perform Complete WordPress Backups And Keep Your Website Regularly Up-To-Date
Never rely on your hosting provider for site backups. Instead, learn how to maintain your WordPress site or get this done for you and develop a habit of performing a full WordPress site maintenance routine frequently (e.g. weekly, monthly, etc …)
A complete WordPress maintenance routine ensures that:
- All unnecessary files and data are removed,
- All WP files and data are free of errors, optimized and backed up,
- All WP software, themes and plugins are up-to-date,
- etc …
A proper WordPress maintenance routine looks like this …
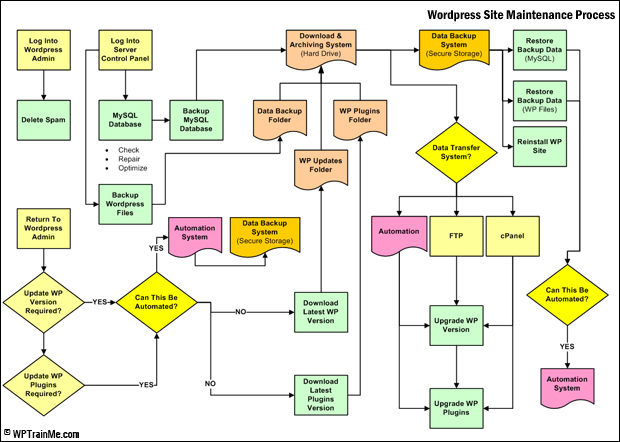 (Maintaining your WP website regularly backed up and updated is vitally important for WordPress security. Source: WPTrainMe.com)
Again, we cannot stress enough how important it is to maintain your WordPress installation fully backed up and updated. WordPress site maintenance is not hard to do or time-consuming, but it must be done to ensure the security of your website or blog. If you don’t want to learn how to do WP site maintenance yourself, pay a professional to do it but make sure it gets done. Backing up your site is the next most important thing you must do after making sure that you still have a pulse!
If you don’t want to perform manual backups, there are a number of plugins you can use. You can read about a WordPress backup plugin that can automate your backup process here: Back Up, Clone & Protect Your WordPress Web Site With Backup Creator WP Plugin
Security Measure #3 – Make Sure That Your Username Is Not “Admin”
The mass brute force attack on WordPress sites was mostly an attempt to compromise site administrator panels by exploiting WordPress sites that used “admin” as their user name.
For website security reasons, avoid installing a WordPress site with the username admin. This is the first area of potential vulnerability hackers will test. If your blog’s username is “admin”, then make sure you change it immediately.
We have created a simple step-by-step tutorial on how to change your admin username here: Changing Your WordPress Admin User Name
Security Measure #4 – Avoid Weak Passwords
A “brute force” attack occurs when malicious software continually and persistently hits a login or password field with different character strings in an attempt to guess the right combination that will give them access to your site.
Unless some measure is put into place to prevent the brute-force attack (see further below for a couple of effective suggestions for doing this), the “bot” will just persist in attacking your site until it eventually gets access.
Weak passwords, therefore, make really easy targets for hacking attacks. Make sure that you change your password to a string containing at least 8 characters long, with upper and lowercase letters, combined with a few “special” characters (e.g. %, #, *, etc).

You can use a password tool like Roboform to help you generate difficult passwords …
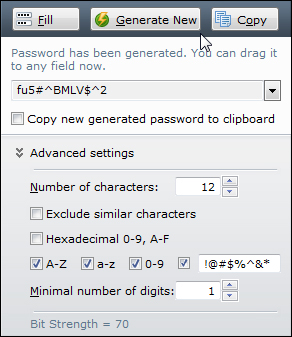 (You can use a password management software tool like Roboform to help you generate strong login passwords)
For a simple tutorial created especially for non-technical WordPress admin users that shows you how to change your password, go here: What To Do If You Need To Reset Your Password
Security Measure #5 – Prevent The wp-config.php File From Being Easily Found
The wp-config.php file allows WordPress to communicate with the database to store and retrieve data and is used to define advanced options for WordPress.
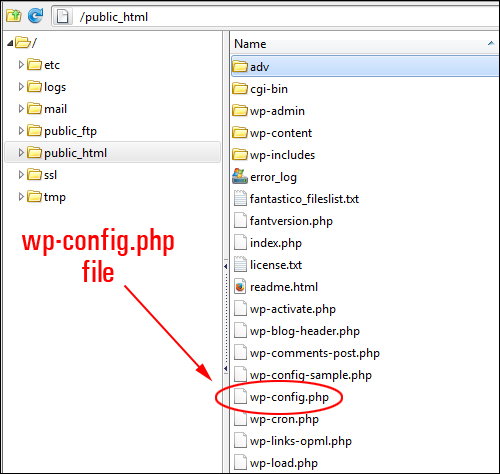
(wp-config.php)
If hackers break into your website, they will typically try to access your wp-config.php file, because this file contains important information about your site’s database, security keys, etc. Getting access to this information would allow someone to change anything in your database, create a user account, upload files and take control of your site.
To protect your WordPress site from being attacked and even being used as part of a bot net, therefore, you must prevent your wp-config.php file from being accessible. This requires knowing how to edit database information, move files around in your server and changing access permissions.
Security Measure #6 – Rename Or Delete Unnecessary Installation Files
Delete or rename your install.php, upgrade.php and readme.html files.
These files are not required after installation. If you don’t want to delete these files, then just rename them.
Security Measure #7 – Update Your WordPress Files, Themes And Plugins
Hackers are always on the lookout for vulnerabilities in earlier versions of WordPress that can be exploited, including outdated versions of WordPress plugins and themes.
Make sure to keep your installation files, themes, plugins, etc. up-to-date.
Security Measure #8 – Disable The WordPress Theme Editor
WordPress installations come with a built-in editor that lets administrators edit theme and plugin code from the dashboard.
You can access your WordPress Theme Editor by selecting Appearance > Editor from your main menu …
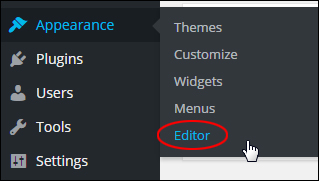
(Accessing the WordPress theme editor using the admin menu)
The WordPress theme editor allows anyone accessing your site’s admin to see and modify all of your WordPress theme files, or cause mayhem on your site.
To prevent people from accessing the WordPress Theme editor, you will need to disable it. This can be done by adding code to your wp-config.php file.
Security Measure #9 – Remove Access To Your Site’s Uploads Directory
The “uploads” folder stores all the media that gets uploaded to your blog.
Normally, this folder is visible to anyone online. All a person needs to do to view all of the contents in the “uploads” folder is navigate to your directory using a web browser …
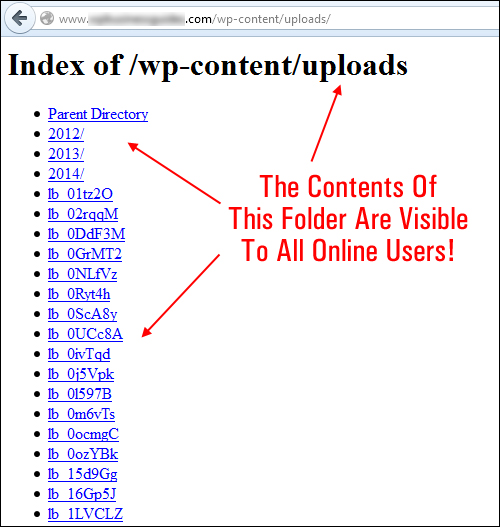
(WordPress has an uploads folder where your media files are stored)
If any directories in your website have vulnerabilities that can be exploited by malicious users, this could become a serious threat to the security of your site.
Protecting your directories will prevent online users from accessing your ‘uploads’ folder and other important directories. This can be done using plugins, setting file permissions, uploading a blank index.php file (this is literally a blank file named “index.php”) to your uploads directory, and so on. Again, it’s best to hire a professional if you are unsure about what to do.
Security Measure #10 – Security Plugins
There are a number of great WordPress security plugins available that specifically address most common security issues WordPress site owners face, such as preventing hackers from accessing your site, protecting your website from malicious scripts, preventing injections of code into files, etc.
Most WordPress plugins address some but not all areas of WordPress security. One security plugin that seems to do a comprehensive job of scanning, fixing and preventing issues that could lead to hackers accessing your website files and causing damage to your site is SecureScanPro.
(SecureScanPro – WordPress complete security software)
SecureScanPro is easy to install and easy to use, and addresses most of the security areas that WordPress users need to address.
Another great plugin you may want to look at using is BlogDefender.
Blog Defender WordPress Security Product Suite
 (Blog Defender)
This product is a package of WordPress security video tutorials, plugins and tools, plus WordPress security documentation in PDF and DOC formats.
BlogDefender shows you where the security holes in your WordPress installation are …
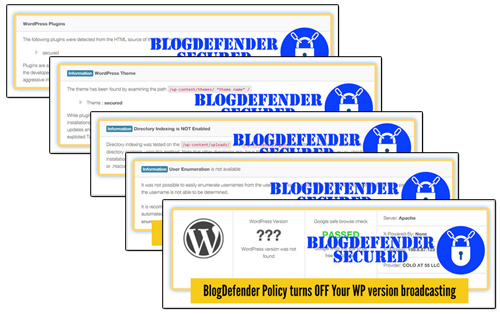
 And then shows you how to fix these quickly and easily …
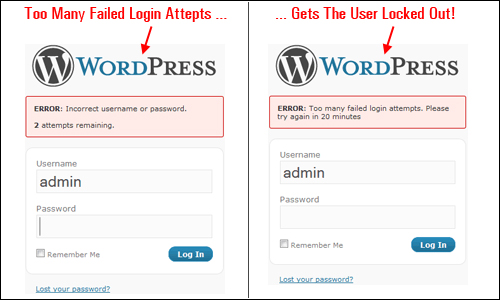
 If you don’t want to purchase a security plugin like SecureScanPro or BlogDefender, then use various free WordPress plugins, such as Limit Login Attempts …
WordPress is a very secure web platform, but neglecting simple maintenance tasks like updating your WordPress software, plugins and themes, tightening file and data protection and taking other necessary precautions can expose your site to attacks by hackers and bots.
Regardless of the type of business you run or plan to run online and how small you think your web presence is, securing your web sites is something you cannot afford to ignore.
As one last reminder of the importance of keeping your websites protected, below is the advice given by an expert on website security to all WordPress users following the mass brute force attacks by botnets on WordPress in 2013 …
Owners of websites based on WordPress CMS must improve at least basic security settings and implement best practices such as the use of robust passwords and the accurate management of “admin” accounts.
Pierluigi Paganini, Chief Information Security Officer, Security Affairs
***
As you can see, WordPress security is very important if you run a WordPress site. Hopefully, this article has shown you what to do to prevent brute-force attacks on your WordPress site. If you need any further help or assistance with WordPress security, please seek help from a WordPress security specialist, or search for a WordPress service provider in our WordPress Services Directory.
We also recommend subscribing to WPCompendium.org to be notified via email whenever we publish new tips on WordPress security and reviews of WordPress security plugins.
***
"Learning WordPress has been a huge stumbling block for me. I've been looking for something that covers absolutely everything but doesn't cost an arm and a leg. Thank you so much ... you have just provided me with what I have been looking for! Truly appreciated!" - Tanya
***