 WordPress often comes under attack by hackers.
In April 2013, WordPress installations around the world were subjected to large-scale brute force attacks.
These attacks were caused by computers infected with viruses and programmed to attack other computers (called “botnets”).
How To Protect Your WordPress Site From A Brute-Force Attack
What Is A Brute-Force Attack?
A brute-force attack is a technique used to break an encryption or authentication system by trying all possibilities.
(Source: Chinese University Of Hong Kong)
One of the many ways hackers will attempt to break into WordPress sites is by trying to guess the site’s administration login username and password. This can be done with scripts and tools that can guess hundreds of possible login combinations in minutes.
If you’re not using strong usernames or unguessable passwords, your website could be easily hacked by repeated attempts to guess your site’s login details.
This is called a “brute-force” login attack.
Botnet Definition
A botnet is a number of Internet-connected computers communicating with other similar machines in an effort to complete repetitive tasks and objectives. This can be as mundane as keeping control of an Internet Relay Chat (IRC) channel, or it could be used to send spam email or participate in distributed denial-of-service attacks. The word botnet is a combination of the words robot and network.
(Source: Wikipedia.org)
”Botnets” are networks of computers that have been compromised and infected with malicious code, which can then be controlled remotely as a group, typically without the computer owners’ knowledge.
Botnets are typically used to send out mass spam emails from the infected computers of compromised user accounts.
Below is a screenshot taken from a site that monitors online security showing the locations of the command centers of ZeuS – a botnet that has been actively infecting computer networks all around the globe since 2009 …
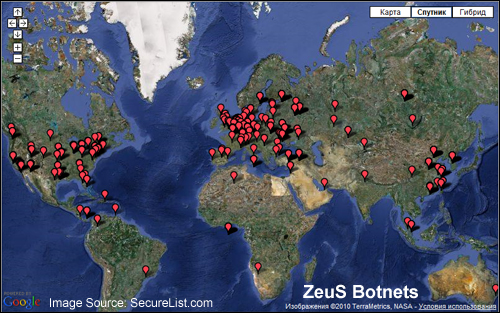
(ZeuS is a botnet that has been actively compromising computer networks all around the world since 2009. Image: SecureList.com)
These were well organized and highly distributed botnet attacks. Over 90,000 IP addresses were identified by a number of webhosting companies in the initial attack, when the web was flooded with millions of attempts to force their way into WordPress users admin areas. The attack continued after this, with over 30,000 WordPress blogs being hacked every day.
News of this brute-force botnet attack was widely reported in all of the major webhosting companiesand leading technology publications, such as TechNews Daily, Forbes, BBC News, PC Magazine, Tech Crunch, and even on the official website of the US Department of Homeland Security …
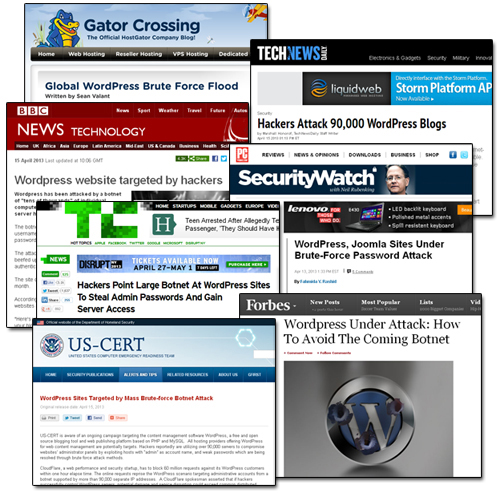
(WordPress powers millions of sites around the world, making it a target for attacks by malicious users)
Does This Mean We Shouldn’t Use WordPress Anymore?
No. In fact, there are lots of great reasons why you should continue using WordPress if you are concerned about the security of your online business.
To understand what makes WordPress a very secure web platform, read this article: Is WordPress A Secure Platform For Websites?

It’s important to understand that, in the case of the brute-force attack described above, was no specific vulnerability in WordPress being exploited (the same script was also attacking sites built using other web platforms like Joomla).
Mike Little, the co-founder of WordPress with Matt Mullenweg, said this about the brute force attacks:
It is a “simple” script that attempts to login using the admin login and a generated password. So if your password is too short or based on dictionary words it will be guessed and then the script can login legitimately and do whatever it wants including installing scripts (as plugins) or editing files. The attack tries to guess your password, if it succeeds, the most secure site in the world is wide open because they have your password.
Preventing Your WordPress Website From Brute-Force Attacks – Ten Security Checks
You may think that your website or blog offers little to no value to hackers, but the reality is that all websites have value to a malicious user.
If a hacker can discover a flaw in your security, that website or blog can then be used to target more valued sites.
Additional undesirable results of being hacked include being blacklisted by search engines, having spammy links advertising things like viagra, cheap offers on brand names, etc. inserted in your content and meta data, malicious redirects to phishing sites and other websites, data exfiltration (stealing customer details or Personal Identifiable Information from your web applications), and lots of other nasty things.
The harsh reality is that malicious bots are most likely scouring for exploits and trying to hack into your website or blog right now. Whether they will hack in or not, depends on how difficult or easy you will make it for them to keep persisting until they can either discover how to get access, or are forced to give up and go look for an easier target.
How Much Information Are You Broadcasting To Hackers About Your WordPress Site?
Do you own a WordPress site? If so, visit a site like Hackertarget.com and run your website through their WordPress security check …
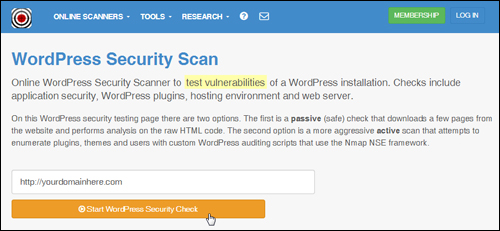 (Hackertarget – WordPress Security Scan Screenshot source: Hackertarget.com)
You will see that the check will yield various results and information about your website setup …
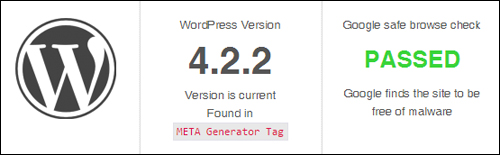
(Hackertarget – WP security check results. Product image: Hackertarget.com)
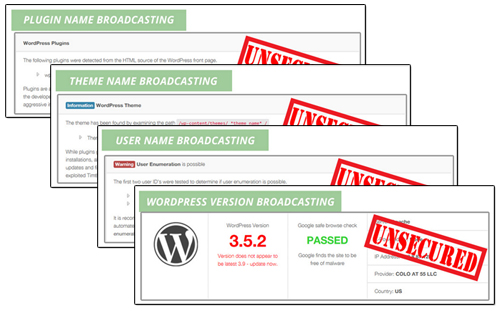
It should be obvious after using the above tool that if you can access all of this information, so can hackers.
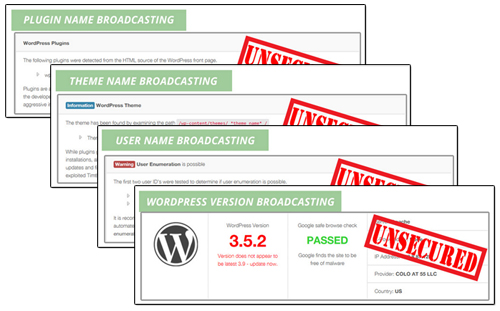 (Product image: BlogDefender.com)
The ability to see which version of WordPress you are using, which plugins and themes you have installed on your site, and which files have been uploaded to certain directories are all valuable information to hackers, as this informs them about any potential security weaknesses, especially where site owners haven’t updated their sites.
If your site or blog is powered by WordPress and you are not proactive steps to toughen up your site, then it’s practically guaranteed that, at some time in the near future, your site will be hacked, or at least targeted by bots, because these brute force attacks are systematically targeting WordPress sites worldwide!
Whenever a site is hacked, website owners will find themselves completely “locked out” of their own site, or notice that their files have been modified or even that their content has been entirely wiped out. Often, sites will be infected with malicious scripts or viruses without the owner even being aware that this has occurred.
To avoid the heartache that comes with having your site being hacked into, below are 10 essential and effective security measures that will help to protect your WordPress site from brute force attacks.

Note: Some of the steps below require some technical skills to modify core WordPress and server files. If you have no web coding skills, or don’t want to mess around with file code, then ask your web host or a professional WordPress service provider for help.
***
Security Measure #1 – Contact Your Host
Get in touch with your webhosting provider and ask them what precautions they have put in place to help prevent your site from being attacked, and what they do to make sure that your server files and data are being backed up.
It’s important to make sure that your webhosting company regularly backs up your server files and that, if disaster strikes, you can easily get back your files and data.
Security Measure #2 – Back Up Your WordPress Data And Files And Keep Your Website Frequently Updated
You should never rely on your webhosting company for your site backups. Instead, learn how to manage your WordPress site or pay someone to get this done for you and maintain a habit of religiously performing a full site maintenance routine on a regular basis (e.g. daily, weekly, fortnightly, etc …)
A full WordPress maintenance routine ensures that:
- All unnecessary data and files are deleted,
- All WP data and files are free of errors, optimized and backed up,
- All themes, plugins and software components are up-to-date,
- etc …
A full WordPress site maintenance routine looks like this …
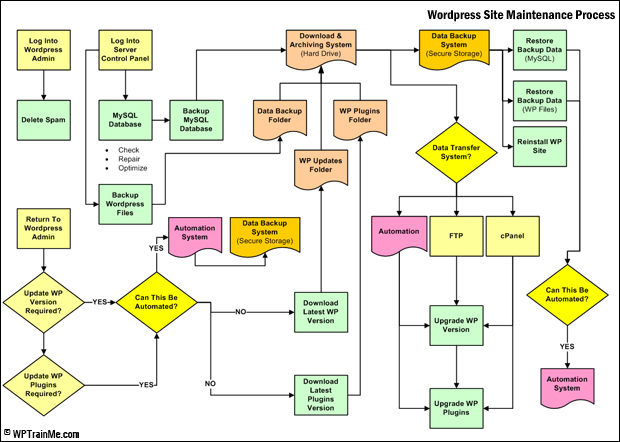 (Maintaining your WordPress website backed up and up-to-date is vitally important for WordPress security. Screenshot image: WPTrainMe.com)
Again, we cannot stress enough how important it is to maintain your WordPress installation backed up and up-to-date. WordPress maintenance is not hard or time-consuming, but it must be done to ensure the security of your website or blog. If you do not want to learn how to do WP site maintenance yourself, get someone else to do it but make sure this gets done. Backing up your site is the next most important thing you should do after making sure that you are still breathing!
If you don’t want to perform manual backups, there are a number of free and paid WordPress plugins you can use. Learn about a WordPress backup plugin that can fully automate your site backups here: Backup, Duplicate And Keep Your WP Site Protected With Backup Creator Plugin For WordPress
Security Measure #3 – Make Sure That Your Username Is Not “Admin”
The mass brute force botnet attack on WordPress is mostly an attempt to compromise website administrator panels and gain access to the site by exploiting sites that used “admin” as the username.
For website security purposes, never install a WordPress site with the username “admin”. This is the first area hackers will test. If your site’s username is admin, then change it immediately.
For a simple tutorial on how to change your WordPress admin username, go here: Changing Your WP Username From Admin To Another User Name
Security Measure #4 – Use Strong Passwords
A “brute force” attack occurs when a malicious script continually and persistently hits a username and password field with different strings of characters in an attempt to guess the right combination that will unlock your website.
Unless you put some measure in place to block the brute-force attack from happening (see further below for a couple of effective ways to do this), the “bot” will just continue to attack your site until it eventually works out the combination.
Weak passwords, therefore, become very easy targets for attacks. Make sure that you change your password to something containing at least eight or nine characters long, with upper and lowercase letters, combined with “special” characters (%^#$@&*).

Roboform is a password software that lets you easily generate different secure login passwords …
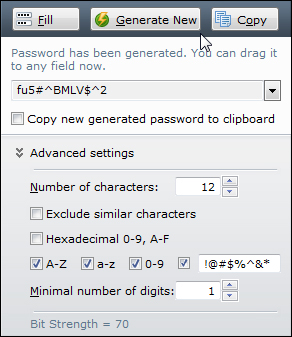 (You can use a password management program like Roboform to generate hard-to-guess passwords)
We have created a simple tutorial that shows you how to change your WordPress admin password here: Changing WordPress Passwords
Security Measure #5 – Prevent Access To The wp-config.php File
The wp-config.php file allows WordPress to communicate with the database to store and retrieve data and is used to define advanced options for WordPress.
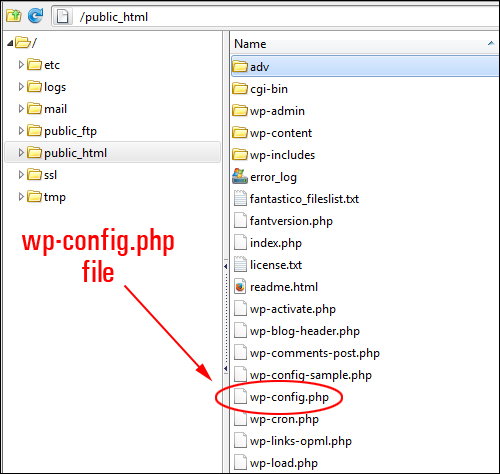
(wp-config.php file)
If a hacker breaks into your WordPress site, they will typically try to access your wp-config.php file, because this file contains your WordPress database details, security keys, etc. Getting access to this information would allow a hacker to change anything in your database, create a user account, upload files and take control of your site.
To protect your WordPress site from being attacked and even being used as part of a bot net, therefore, you must prevent your wp-config.php file from being easily accessible. This requires knowing how to edit database information, move files around in your server and changing access permissions.
Security Measure #6 – Delete Or Rename Unnecessary Installation Files
Rename or delete your install.php, upgrade.php and readme.html files.
You can remove these files after installation. If you don’t want to delete these files, just rename them.
Security Measure #7 – Upgrade Your WordPress Site, Plugins & Themes To Their Latest Version
Hackers look for vulnerabilities they can exploit in outdated WordPress versions, including out-of-date versions of WP plugins and themes.
Make sure to always keep your software files, plugins, themes, etc. up-to-date.
Security Measure #8 – Disable The WordPress Theme Editor
WordPress comes with a built-in editor feature that lets you edit theme and plugin code from the dashboard area.
You can access the WordPress Theme Editor by selecting Appearance > Editor in the dashboard menu …
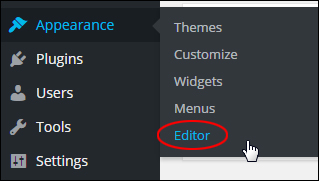
(The WordPress theme editor can be accessed via the dashboard menu)
The WordPress theme editor lets anyone accessing your blog’s admin area view and change your WordPress theme files, or create mayhem on your site.
If you want to prevent people from being able to access your WordPress Theme editor, you will need to disable it. This can be done by editing your wp-config.php file.
Security Measure #9 – Prevent Access To Your WordPress Uploads Directory
The WordPress “uploads” folder contains all the media that gets uploaded to your WordPress site.
Normally, this folder is visible to online users. All a person needs to do to see the contents in your “uploads” folder is navigate to your directory using their browser …
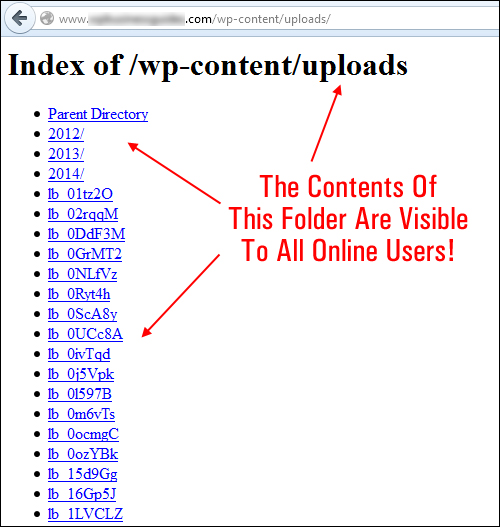
(WordPress uploads directory)
If any files stored in his folder have weaknesses or vulnerabilities that can be exploited by hackers or malicious users, this can compromise the security of your site.
Protecting your directories will prevent unauthorized people from viewing your ‘uploads’ folder and other important directories. This can be done using plugins, setting file permissions, uploading a blank index.php file (this is literally an empty file named “index.php”) to your uploads directory, and so on. Again, it’s best to consult a professional if you are not sure about what to do.
Security Measure #10 – Use Security Plugins
There are a number of great WordPress security plugins available that will address most common security issues WordPress website owners face, such as preventing hackers from accessing your site, protecting your site from malicious software, preventing injections of code into files, etc.
Most WordPress plugins address some but not all areas of WordPress security. One plugin that does a comprehensive job of scanning, fixing and preventing potential issues that could lead to hackers accessing your website files and causing damage to your site is SecureScanPro.
(SecureScanPro – complete security software for WordPress)
SecureScanPro is easy to install and easy to use, and fixes most of the security issues that WordPress users need to address.
Another great security plugin you may want to consider using is BlogDefender.
Blog Defender Security Suite For WordPress Sites
 (Blog Defender WordPress Security Plugin)
Blog Defender is a package of WordPress security video tutorials, plugins and tools, plus a WordPress security PDF/DOC file.
BlogDefender scans you WordPress installation for potential security holes …
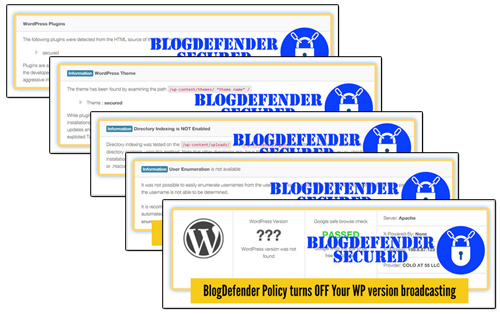
 And lets you fix these quickly and easily …
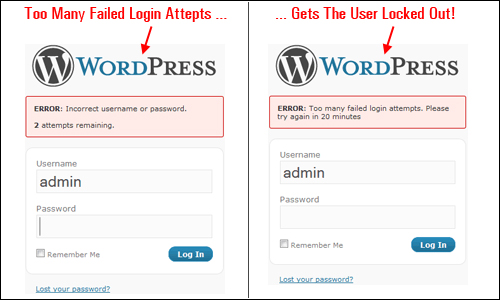
 If you don’t want to buy a premium security plugin like SecureScanPro or BlogDefender, then use various free WP plugins, such as Limit Login Attempts …
WordPress is a very secure web platform, but neglecting essential maintenance tasks like updating your WordPress software, WordPress plugins and WP themes, tightening file and data security and taking other necessary precautions can expose your site to attacks by hackers and bots.
Regardless of the kind of business you run or plan to run online and how small you think your web presence is, you simply cannot ignore the importance of website security.
As a final reminder, below is the advice given by an expert on web security to all WordPress users following the mass brute-force attacks on WordPress in April 2013 …
Owners of websites based on WordPress CMS must improve at least basic security settings and implement best practices such as the use of robust passwords and the accurate management of “admin” accounts.
Pierluigi Paganini, Chief Information Security Officer, Security Affairs
***
As you can see, WordPress security is very important if you run a WordPress site. Hopefully, the information in this article will help prevent brute force attacks on your WordPress site. If you need any further help or assistance with WordPress security, please consult a professional WordPress security specialist, or search for a professional WordPress service provider in our WordPress Services Directory.
We also recommend subscribing to WPCompendium.org to receive notifications via email when we publish new articles and tutorials on WordPress security and reviews of new security plugins.
***
"Wow! I never knew there's so much to learn about WordPress! I bought one of the WordPress for Dummies three years ago, such authors need to be on this course!" - Rich Law, Create A Blog Now
***