 In 2013 a global brute force attack hit WordPress installations across almost every host server in existence.
These attacks were caused by botnets (computer networks infected with malware and programmed to attack other vulnerable computers).
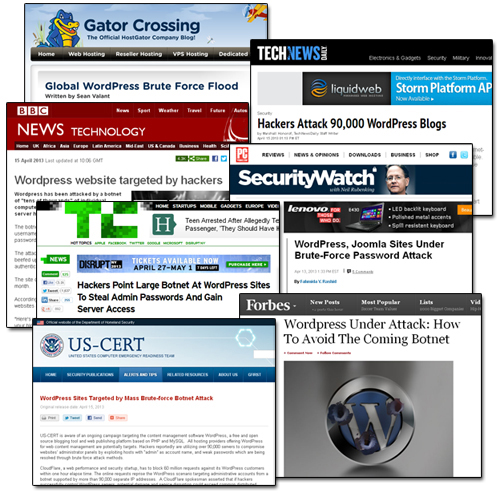
(Being the world’s most used CMS makes WordPress an obvious target for attempted hacking attacks)
On March 11, 2014, many leading technology sites began reporting that over 162,000 WordPress websites had been hacked.
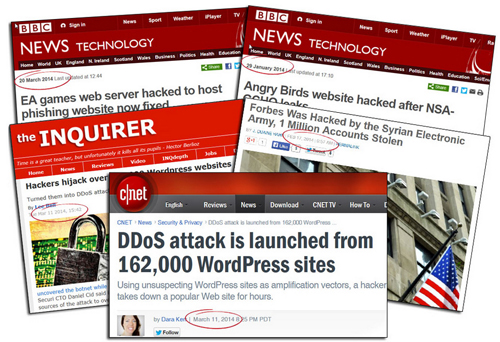
(160,000+ WordPress sites were attacked in a massive DDoS attack in early 2014. Screenshot image: Blog Defender)
According to the Cnet report,
“With some old-fashioned trickery, hackers were able to get more than 162,000 legitimate WordPress-powered Web sites to mount a distributed-denial-of-service attack against another Web site.”
(Source: cnet.com/news/ddos-attack-is-launched-from-162000-wordpress-sites)
As described by security firm Sucuri, hackers had leveraged a well-known flaw to attack unsuspecting WordPress sites and direct a distributed-denial-of-service cyber attack (DDoS) towards another popular website.
When attacks on WordPress sites happen, it’s natural for website owners to question if WordPress really is a safe platform for running an online presence.
Powering millions of websites and blogs around the world makes WordPress an obvious target for hacking attacks. But do you need to be concerned about WordPress as a secure platform for building your business website?
In this article, you will learn some of the main reasons why you should definitely choose WordPress if you have any concerns about website security.
WordPress Security Explained
Let’s start with the facts …
Thousands of websites are attacked every year … not just WordPress sites!
The sheer number of attacks on websites and blogs worldwide is rising, and this is only going to get worse.
It’s probably safe to assume that if you haven’t been hacked yet, then it’s only a matter of time … regardless of the web platform you use!
Since it’s no longer a matter of if, but a matter of when before your website is targeted by malicious hackers, are there any advantages that WordPress can offer you in terms of security?
How Secure Are “Open Source” Software Applications?
Many people often argue that WordPress should not be used for building and running a business online because it is “open source” and freely available software application.
Open source CMS software like WordPress, Drupal and Joomla are free to use and anyone can view the underlying code.
The argument against using WordPress, then, goes something like this: If everyone can examine the Open Source software code for WordPress, then hackers can easily get hold of the code and study every single line in great detail, searching for holes and weaknesses in the code that can be exploited …
(It’s not a matter of if, but a matter of when before your website will be targeted by malicious hackers … WordPress or no WordPress!)
While it’s true that WordPress is a free program and hackers can easily access it and study the code searching for vulnerabilities and weaknesses (hackers can do the same with any software program), the fact that WordPress is a free, open-source platform actually makes it a whole lot more secure in many ways.
This is because WordPress is supported by a large community that consists of thousands of people such as software programmers, plugin developers and theme designers who are constantly working to help improve the software and make WordPress more secure …
(A huge volunteer community build and maintain. Screenshot: WordPress.org)
WordPress continually evolves through the effort of a huge volunteer community working around the clock to fix any issues detected by users. It benefits from thousands of individuals committed to improving the software, identifying and fixing security issues and making the WordPress platform safer for every user …
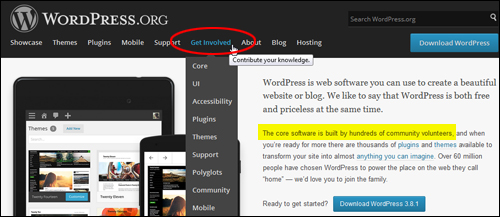
(The WordPress core software is built by a large community of volunteer web developers. Screenshot: make.wordpress.org)
The moment that any security problem is discovered by developers or users, these are immediately logged in user forums and addressed by the WordPress development team …
(WordPress is continually being improved upon by thousands of committed individuals community of developers and users. Image source: WordPress.org)
The WordPress community support system, therefore, is quite formidable and anyone can contribute to the improvement of the platform.
For example:
- If you find bugs or security vulnerabilities, you can report these by notifying security@wordpress.org.
- If you find any issues in a WordPress plugin, you can also report these by sending an email to plugins@wordpress.org.
This is one of the reasons why the WordPress team releases new version updates so often, and why you need to keep your WordPress site updated …
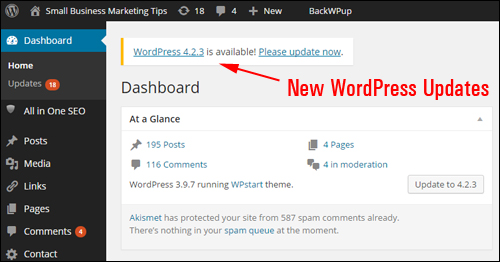
(WordPress frequently releases new updates to plug any security holes found)
WordPress Vs Proprietary CMS Platforms
We’ve just seen that one of the security advantages of using an open source technology like WordPress is that users benefit from a large community of developers who continually contribute to improve platform security. By contrast, proprietary or “closed-source” software applications are normally built by a small team of developers with limited time and resources to provide continuous security monitoring, software maintenance, bug fixes and updates.
The WordPress CMS is free to download, use and modify, and hundreds of volunteers and expert developers are continually working to improve the platform. Can a proprietary CMS company afford to employ as many developers and programmers and still deliver users a completely free application that they can download, use and modify as they wish?
WordPress Vs Other Open Source CMS Platforms
(CMS Platforms)
Whilst on the topic of Open Source content management applications, research shows that the WordPress CMS is actually safer than other Open Source CMS platforms such as Drupal and Joomla.
For example, the chart below shows how many security vulnerabilities were found in each of these open source platforms during a certain period …
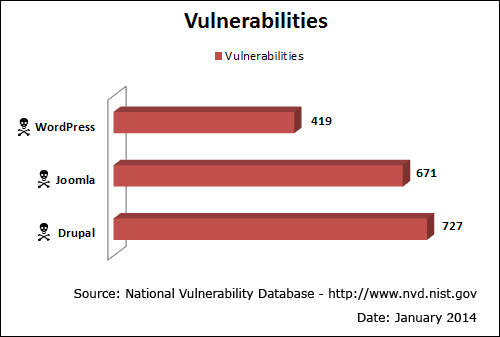
(WordPress experiences less security vulnerabilities than other leading CMS applications. Screenshot image: National Vulnerability Database)
Other studies also show that, because WordPress is easy to use and to maintain, when sites across different CMS platforms were tested for security issues, WordPress sites had significantly less exposure to risk …
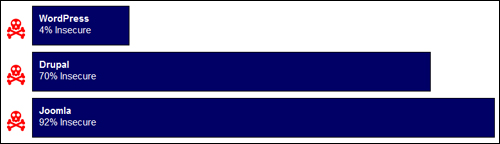
(Blog Defender – CMS Tests. Screenshot source: BlogDefender.com)
WordPress Is Not To Blame
When WordPress sites get attacked en masse, don’t be quick to blame the WordPress CMS platform.
According to a report called “Compromised Websites: An Owner’s Perspective,” which is published by security vendor Commtouch and StopBadware, a nonprofit organization that helps webmasters identify, remediate and prevent website compromises, a large number of webmasters are not fully aware of the security threats their websites are exposed to, how to properly secure a website, or how to deal with compromises.
In fact, over sixty percent of webmasters surveyed for the report didn’t even know how their websites had been compromised by hackers after an attack …
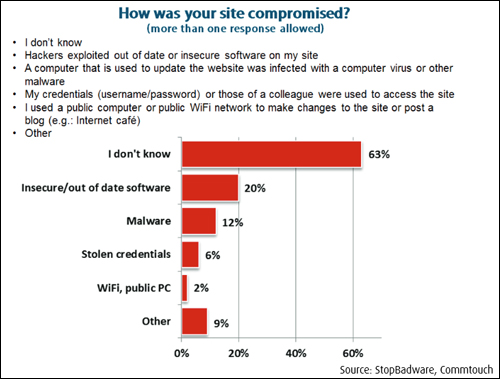
(Many webmasters don’t even know how their sites were hacked. Source: StopBadware.org)
Of immediate concern, however, is the fact that many security-related issues result from users running WordPress on outdated versions of the software …
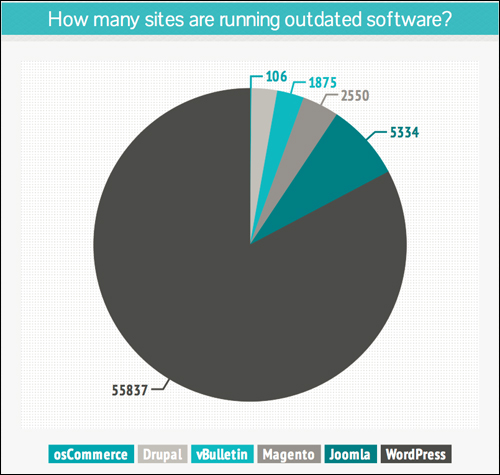
(Many WordPress sites are running on outdated versions. Image source: Sucuri.net)
When WordPress security issues were looked at in more detail, it was found that only around between 20% – 35% percent of vulnerabilities discovered in 3rd-party code are found in the WordPress CMS core, while most security issues are found in plug-ins and extensions …
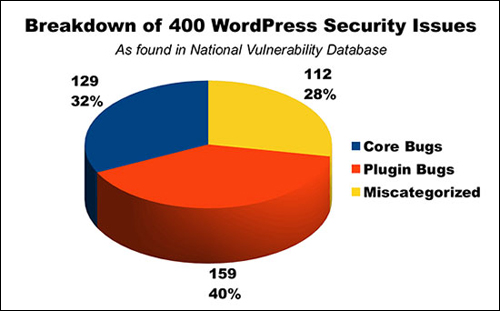
(WP Security Issues. Source: WebDesign.org)
Like all robust software platforms, WordPress is updated regularly in order to deal with new security problems that may arise. Improving software security is an ongoing concern, and to that end, you should always keep your WordPress software, themes, and plugins updated to the latest version.
WordPress Is Secure – Just Ask Any Bank Using It!
The amount of misinformation about WordPress security has even caused Matt Mullenweg, the co-founder of WordPress, to chime into the online discussion.
In a post entitled “A Bank Website on WordPress” posted on April 15, 2015, Matt wrote the following about WordPress security …
There’s a thread on Quora asking “I am powering a bank’s website using WordPress. What security measures should I take?” The answers have mostly been ignorant junk along the lines of “Oh NOES WP is INSECURE! let me take my money out of that bank”, so I wrote one myself, which I’ve copied below.
I agree there’s probably not a ton of benefit to having the online banking / billpay / etc portion of a bank’s website on WordPress, however there is no reason you couldn’t run the front-end and marketing side of the site on WordPress, and in fact you’d be leveraging WordPress’ strength as a content management platform that is flexible, customizable, and easy to update and maintain.
Matt then goes on to provide a couple of security tips, before stating the following …
For an example of a beautiful, responsive banking website built on WordPress, check out Gateway Bank of Mesa AZ. WordPress is also trusted to run sites for some of the largest and most security-conscious organizations in the world, including Facebook, SAP, Glenn Greenwald’s The Intercept, eBay, McAfee, Sophos, GNOME, Mozilla, MIT, Reuters, CNN, Google Ventures, NASA, and literally hundreds more.
As the most widely used CMS in the world, many people use and deploy the open source version of WordPress in a sub-optimal and insecure way, but the same could be said of Linux, Apache, MySQL, Node, Rails, Java, or any widely-used software. It is possible and actually not that hard to run WordPress in a way that is secure enough for a bank, government site, media site, or anything.
Millions of businesses choose WordPress to build their web presence, including banks, leading brands, and e-commerce sites, not just bloggers.
Other Factors Affecting Security
Other areas that can affect site security include:
- No platform is immune to hackers. As many as 90% of all websites across all platforms are vulnerable to being attacked, mostly due to using software that is out of date.
- The biggest security vulnerability of all content management platforms seems to be the users themselves. For example, many users ignore good password security practices.
- Lack of constant monitoring. All security processes require frequent monitoring, testing, updating and improvement.
- Server setup. For example, websites on shared webhosting are only as safe as the least secure site on the hosting grid, so if someone else on your shared server gets their site broken into, then every site on that server is potentially vulnerable to being hacked also.
There’s No Reason Why You Should Not Use WordPress
As you can see, WordPress is a secure web platform. As long as you commit to implementing basic web security measures and keep your WordPress software (and plugins, themes, etc.) updated, there’s really no reason to avoid using WordPress to run your web site or blog.

WordPress Security – Tips
To learn about ways to protect your WordPress site from brute-force attacks see this article: 10 Security Measures That Can Prevent Brute Force Attacks On WordPress
A compromised blog provides hackers with a valuable platform for distributed attacks, spreading malware and engage in information theft. Blog Defender Security Plugin makes your WordPress site invisible to attacks from hackers and botnets. Learn more about this plugin here:
If you are currently using an older WordPress version make sure you back up your WordPress website fully before updating your software to benefit from the latest security updates. This way, if things don’t go as planned, you can always restore.
If you don’t want to perform manual backups, there are a number of WordPress plugins you can use. You can read about a WordPress backup plugin that can automate your site backups here: Backup, Clone And Keep Your WordPress Site Protected With Backup Creator WordPress Plugin

Article References
For more information on the above, see the following sources:
- ITProPortal.com
- National Vulnerability Database
- BlogDefender.com
- UpAndUpStudios.com
- StopBadware.org
- Sucuri.net
- WebDesign.org
- Quora.com
- Ma.tt
Hopefully, now you have a better understanding of problems that can affect your website and how WordPress can help you get better business results online. To learn more about using WordPress for a business website please see other posts we have published on this site or subscribe to receive updates and notifications when new articles or tutorials are published.
***
"I am beyond impressed with what you have put together. I can tell that you put a ton of hard work into building what you have. You have the absolute best content on WordPress I have ever seen!" - Robert T. Jillie