 Being the world’s most used content management system makes WordPress a target for hacker attacks.
In April 2013 a global brute-force attack hit WordPress installations across almost every WP host server in existence.
These attacks were caused by computer networks infected with viruses and programmed to attack other vulnerable computers, also commonly known as “botnets”.
How To Protect Your WordPress Site From A Brute-Force Attack
Brute-Force Attacks
A brute-force attack is a technique used to break an encryption or authentication system by trying all possibilities.
(Source: Chinese University Of Hong Kong)
There are many ways hackers try to break into a WordPress site. One of these is by trying to guess the site admin’s login username and password. This can be done with software tools and scripts that can guess hundreds of possible logins in minutes.
If you’re using predictable user names and predictable passwords, your website could be an easy target for hackers.
This is called a “brute-force” login attack.
Botnets
A botnet is a number of Internet-connected computers communicating with other similar machines in an effort to complete repetitive tasks and objectives. This can be as mundane as keeping control of an Internet Relay Chat (IRC) channel, or it could be used to send spam email or participate in distributed denial-of-service attacks. The word botnet is a combination of the words robot and network.
(Source: Wikipedia.org)
”Botnets” are networks of private computers that have been compromised and infected with malicious software, which can then be controlled remotely as a group, typically without the computer owners’ knowledge or awareness.
Botnets are normally used used to send mass spam emails.
Below is a screenshot taken from a site that monitors online security showing the locations of the command centers of ZeuS – a botnet that has been actively infecting computer networks all around the globe since 2009 …
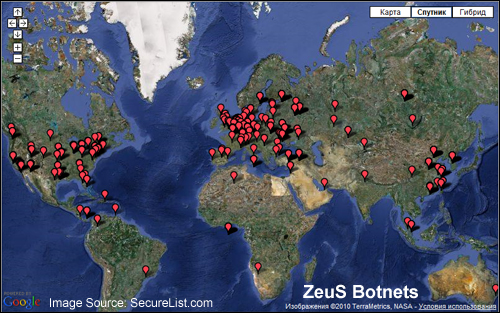
(The Zeus botnet has been actively compromising computer networks all around the world since 2009. Screenshot: SecureList.com)
These ongoing botnet attacks on WordPress sites were highly distributed and well organized. Over 90,000 IP addresses were identified by a number of webhosting companies in the initial attack alone, when millions of attempts to force their way into WordPress users administration areas took place. The large-scale brute force attacks continued after this, with over 30,000 WordPress sites and blogs being hacked each day.
Coverage of the worldwide brute-force botnet attack was widely reported in all the major webhosting companiesand leading technology media publications, such as TechNews Daily, Forbes, BBC News, PC Magazine, Tech Crunch, and even on the official website of the US Department of Homeland Security …
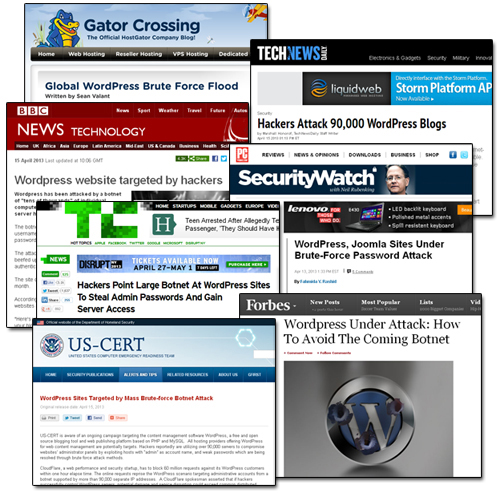
(Being the world’s most used CMS makes WordPress an obvious target for attempted attacks by malicious users)
Does This Mean WordPress Is Not Secure And We Should Stop Using It?
No. In fact, there are many very good reasons why you should continue using WordPress if you are concerned about the security of your website.
To learn what makes WordPress a very secure platform for websites, read this article: How Secure Is WordPress?

It’s important to understand that, in the case of the worldwide brute-force attack described above, no specific WordPress vulnerability was being exploited (the same script was also targeting sites built using other platforms like Joomla).
Mike Little, the co-founder of WordPress, made the following comment about the brute-force attacks:
It is a “simple” script that attempts to login using the admin login and a generated password. So if your password is too short or based on dictionary words it will be guessed and then the script can login legitimately and do whatever it wants including installing scripts (as plugins) or editing files. The attack tries to guess your password, if it succeeds, the most secure site in the world is wide open because they have your password.
Protecting Your WordPress Site From Being Brute-Force Attacked – Ten Security Measures
Every blog with a vulnerability provides some value opportunity to hackers. If you think that your website offers little to no value to hackers, think again. Business websites, personal blogs, government sites … even web sites owned by web security experts can and have been targeted.
If someone can discover a vulnerability in your security setup that allows them to access and take over your blog, the website can then be used to target other valuable web sites.
Additional undesirable consequences of being hacked and your site security compromised include being blacklisted by Google, having spammy links promoting things like online meds, discounted fashion, etc. inserted in your content and meta data, redirecting visitors to phishing sites, drive-by downloads (adding malicious software on your visitors’ computers), and lots of other nasties.
The reality is that malicious bots are probably trying to break into your web site while you are reading these very words. Whether they can do this successfully or not, depends on how hard you will make it for them to keep trying until they either can find how to get in, or are forced to give up and decide to look for a more vulnerable target.
How Much Information Are You Broadcasting To Hackers About Your Site?
Does your website run on WordPress? If so visit a site like Hackertarget.com and run your website through their WordPress security check …
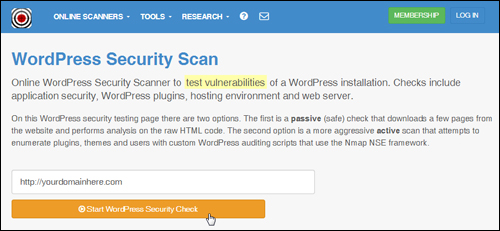 (Hackertarget – Website Security Scan Screenshot source: https://hackertarget.com/wordpress-security-scan)
You will see that the test will return various results and information about your WordPress site …
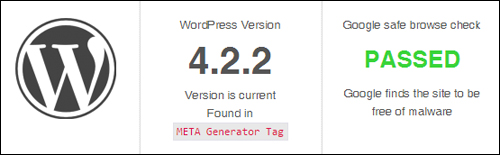
(Hackertarget – website security scan results. Product image: Hackertarget.com)
It should be obvious after using the above tool that if you can access all of this information about your site, hackers can too.
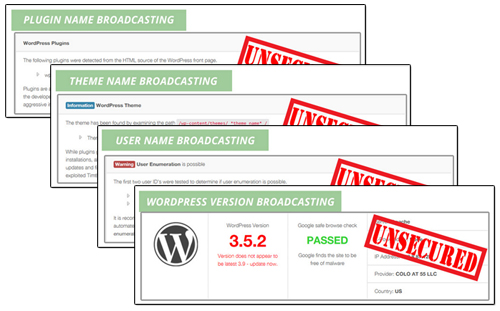 (Image source: Blog Defender)
The ability to see which version of WordPress you are using, which plugins and themes you have installed, and which files have been uploaded to certain directories can be potentially valuable information to hackers, as this informs them about any exploitable holes or weaknesses, especially in older versions.
If your site or blog is powered by WordPress and you are not preventive steps to bolster the security of your site, then it’s practically guaranteed that, at some time in the near future, your site will be hacked, or at least targeted by bots, because these brute-force attacks are systematically targeting WordPress installations worldwide!
When a site gets broken into, site owners can discover much to their dismay that they have been “locked out” of their own site, or notice that their content has been interfered with or that everything has been entirely wiped out. Often, compromised sites will be infected with malicious software without the owner even being aware that a security breach has occurred.
To help avoid the heartache and aggravation (and significant financial loss) of having your site being hacked into, below are 10 simple, yet essential and effective security checks that will help to prevent your WordPress site from brute force attacks.

Note: A few of the recommended steps below need some technical understanding of how to modify core WordPress or server files. If you lack these technical skills, or don’t want to mess around with file code, then ask your web host or a professional WordPress technical provider for assistance.
***
Security Measure #1 – Get In Touch With Your Web Host
Contact your webhosting service provider and ask them exactly what systems they offer to protect your site from being attacked, and what they do to ensure that your server files and data get backed up.
Make sure that your webhosting service backs up your server files and that, if disaster strikes, you can quickly and easily get your files and data back.
Security Measure #2 – Perform Full WordPress Backups And Keep Your Website Regularly Updated
You should never rely just on your web host for site backups. Instead, learn how to maintain your WordPress site or pay someone to get this done for you and develop a habit of religiously performing a complete WordPress site maintenance routine frequently (e.g. weekly, fortnightly, etc …)
A proper WordPress maintenance routine ensures that:
- All unnecessary data and files are removed,
- All WP files and data are free of errors, optimized and backed up,
- All software, themes and plugins are up-to-date,
- etc …
A complete WordPress maintenance routine looks like this …
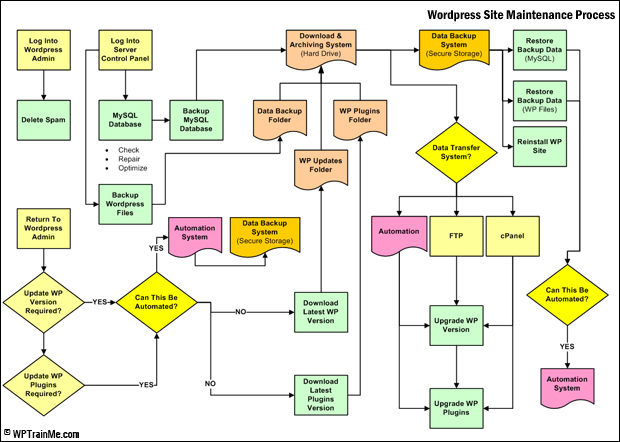 (Maintaining your WordPress web site frequently backed up and updated is vitally important for WordPress security. Image source: WPTrainMe.com)
Again, we cannot stress enough how vitally important it is to maintain your WP site completely backed up and updated. WordPress maintenance is not hard or time-consuming, but it must be done to ensure the security of your website. If you don’t want to learn how to do WordPress maintenance yourself, get someone else to do it but make sure it gets done. Backing up your website is the second most important thing you should do after making sure that you are still breathing!
If you don’t want to perform manual backups, there are a number of plugins you can use. You can read about a WordPress backup plugin that can fully automate your site backups here: Backup, Copy & Keep Your WordPress Websites Protected With Backup Creator WP Plugin
Security Measure #3 – Do Not Use “Admin” As The Admin Username
The brute force attack on WordPress sites was mostly attempting to compromise site administrator panels and gain access to the site by exploiting WordPress sites using “admin” as their user name.
For website security purposes, avoid setting up WordPress sites with the username admin. This is the first area hackers will test. If your blog’s username is admin, you will should change this immediately.
We have created a simple step-by-step tutorial that shows you how to change your login username here: Changing Your Admin User Name In WordPress
Security Measure #4 – Choose A Strong Password
A “brute force” attack occurs when malicious software persistently tries to guess the right combination of characters in a password and username that will unlock your website.
Unless you put some measure in place to block the brute-force attack from happening (see further below for a couple of simple and effective ways to do this), the “bot” will just continue to attack your site until it eventually breaks into your admin area.
Weak passwords, therefore, become really easy targets for hackers. Make sure that you change your password combination to a string that is at least eight characters long, with upper and lowercase letters, and add a few “special” characters (%^#$@&*).

You can use a password management tool like Roboform to create secure login passwords …
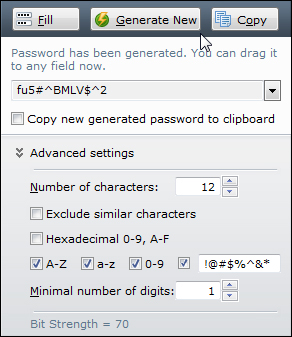 (Roboform is a password management program you can use to generate very secure passwords)
We have created a detailed tutorial that shows you how to change your admin password here: What To Do If You Need To Change Your Password
Security Measure #5 – Prevent The wp-config.php File From Being Visible
The wp-config.php file allows WordPress to communicate with the database to store and retrieve data and is used to define advanced WordPress options.
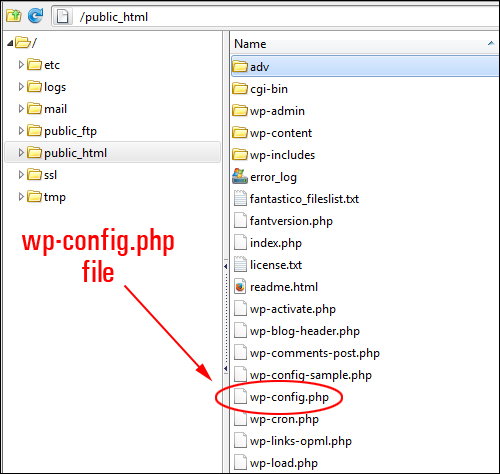
(WordPress WP Config file)
If a hacker breaks into your WordPress website, they will try to access the wp-config.php file, because this is the file that contains your database information, security keys, etc. Getting access to this information would allow someone to change anything in your database, create a user account, upload files and take control of your site.
In order to protect your WordPress site from being attacked and even being used as part of a bot net, therefore, you must prevent your wp-config.php file from being easily accessed. This requires knowing how to edit database information, move files around in your server and changing access permissions.
Security Measure #6 – Delete Or Rename Unnecessary Installation Files
Delete or rename the install.php, upgrade.php and readme.html files from your server.
You can remove these files after installation, as they are unnecessary. If you don’t want to delete these files, then just rename them.
Security Measure #7 – Upgrade Your WordPress Software, Plugins And Themes To Their Latest Version
Hackers look for vulnerabilities in outdated versions of WordPress that can be exploited, including outdated versions of WordPress plugins and themes.
Make sure to always keep all of your software files, themes, plugins, etc. up-to-date.
Security Measure #8 – Disable The Theme Editor
WordPress installations come with a built-in editor that lets administrators edit theme and plugin files from the dashboard area.
You can access your WordPress Theme Editor by selecting Appearance > Editor from your admin menu …
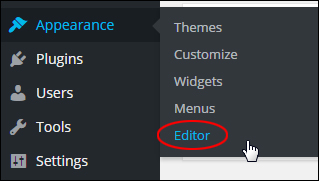
(Accessing the WordPress theme editor via the dashboard menu)
The WordPress theme editor lets anyone accessing your blog’s admin view and change your WordPress theme template files, and cause mayhem on your site.
If you want to prevent unauthorized people from accessing the WordPress Theme editor, you will need to disable it. This can be done by editing your wp-config.php file.
Security Measure #9 – Remove Access To The Site’s Uploads Directory
The WordPress “uploads” directory stores all the media that gets uploaded to your WordPress site.
By default, this folder is visible to online users. All someone has to do to view all of the contents in your “uploads” folder is navigate to your directory using their web browser …
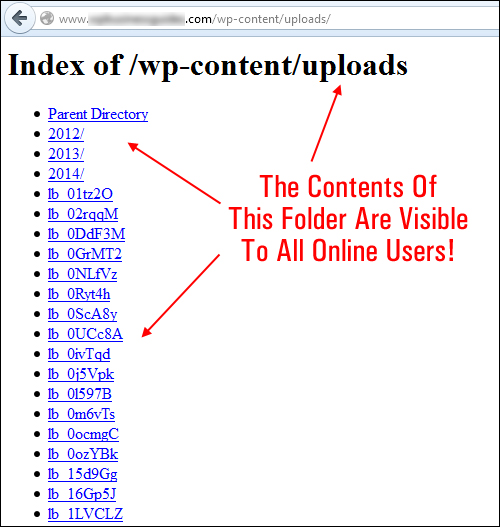
(WordPress has an uploads folder where your media files are stored)
If any directories in your website have vulnerabilities that can be exploited by malicious users, someone could upload unauthorized file types to your site.
Protecting your directories will prevent unauthorized people from viewing your ‘uploads’ folder and other important directories. This can be done using plugins, setting file permissions, uploading a blank index.php file (this is literally a file with nothing in it named “index.php”) to your uploads directory, and so on. Again, it’s best to ask for assistance from someone with experience if you are unsure about what to do.
Security Measure #10 – WordPress Security Plugins
There are a number of great security plugins for WordPress available that specifically address most security issues faced by WordPress site owners, such as preventing hackers from gaining access to vital information about your site, protecting your files from malicious software, preventing injections of code into files, etc.
Most WordPress plugins address some but not all areas of WordPress security. One WordPress plugin that does a comprehensive job of scanning, fixing and preventing potential issues that could lead to hackers accessing your files and causing damage to your site is SecureScanPro.
(SecureScanPro – WordPress complete security software)
SecureScanPro is easy to install and easy to use, and takes care of most of the security issues that WordPress users need to address.
Another great plugin you may want to consider using is BlogDefender.
Blog Defender
 (Blog Defender Security Solution For WordPress)
This product is a package of WordPress security video tutorials, plugins and tools, plus WordPress security documentation in PDF and DOC formats.
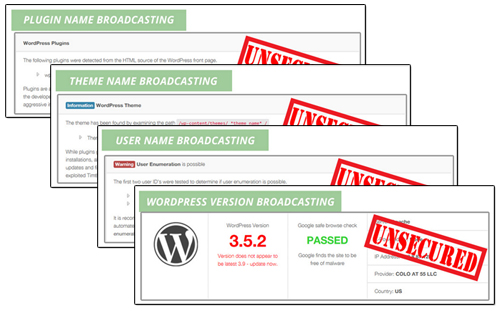
BlogDefender shows you where potential security weaknesses in your WordPress installation are …
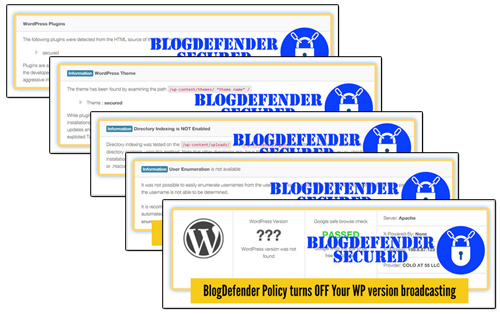
 And lets you quickly and easily fix these …
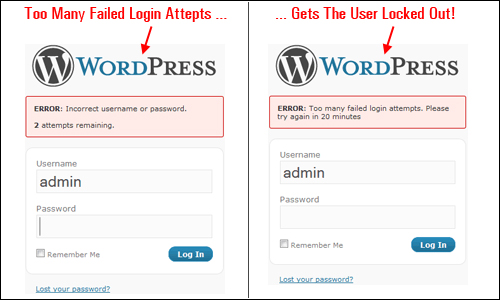
 If you don’t want to buy a security plugin like SecureScanPro or BlogDefender, then use various free plugins, such as Limit Login Attempts …
WordPress is a secure platform, but neglecting essential maintenance tasks like keeping your WordPress core files, plugins and WP themes up-to-date, tightening file and data security and taking other necessary precautions can expose your site to attacks by hackers and bots.
Regardless of the kind of business you run or plan to run online and how small you think your web presence is, you simply cannot afford to ignore the importance of web security.
As one last reminder, below is the advice given by a security expert to all WordPress users after the large-scale brute-force attacks by botnets on WordPress in April 2013 …
Owners of websites based on WordPress CMS must improve at least basic security settings and implement best practices such as the use of robust passwords and the accurate management of “admin” accounts.
Pierluigi Paganini, Chief Information Security Officer, Security Affairs
***
As you can see, WordPress security is of the utmost importance if you run a WordPress site. Hopefully, this information has shown you what to do to prevent brute force attacks on your WordPress site. If you need any further help or assistance with WordPress security, please consult a professional WordPress security specialist, or search for a WordPress technical provider in our WordPress Services Directory.
We also recommend subscribing to WPCompendium.org to be notified whenever we publish new articles and tutorials on WordPress security and tutorials about new WordPress security plugins.
***
"I am beyond impressed with what you have put together. I can tell that you put a ton of hard work into building what you have. You have the absolute best content on WordPress I have ever seen!" - Robert T. Jillie
***